You might not expect a disaster recovery company to weigh in on business email compromise (BEC). But the fact that we are the ones talking about it is a sign that, too often, something’s gone wrong.
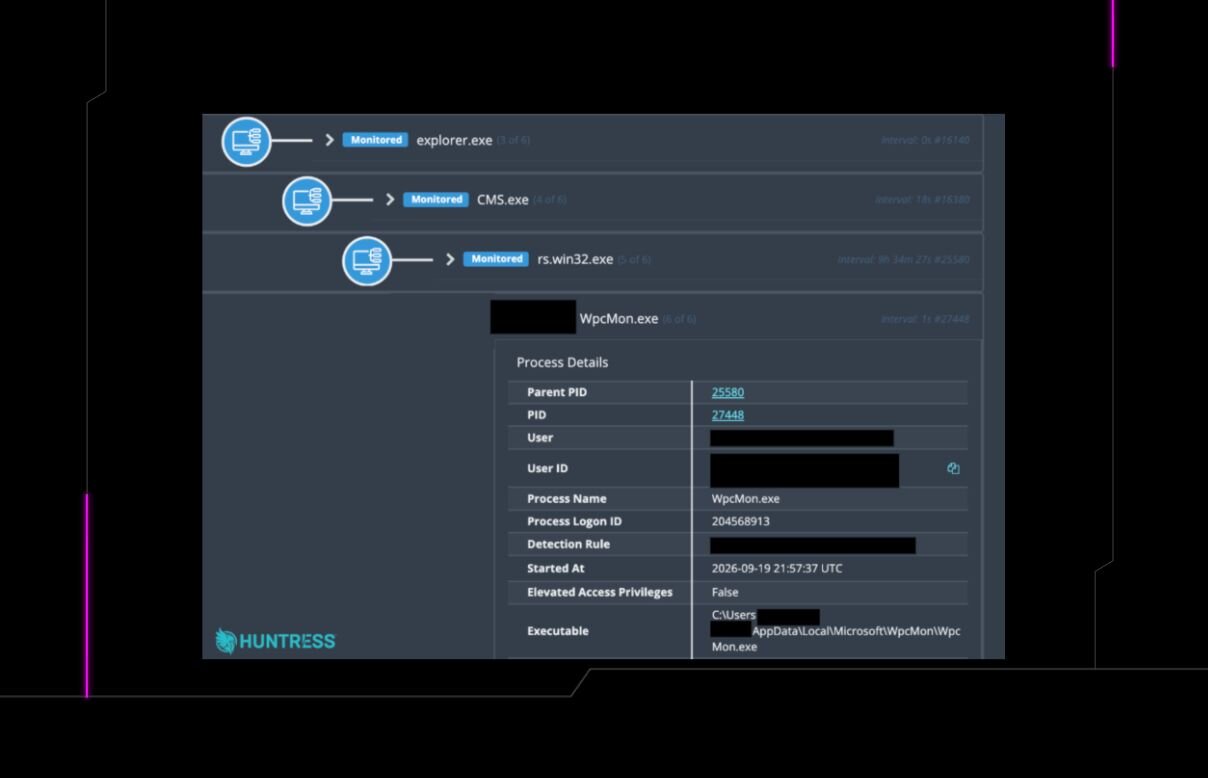
Attackers compromised camera management software to deploy malware, establish persistence, and beacon to C2. Huntress breaks down the attack chain and IOCs.
A Google search for Amazon business led to a ClickFix lure that dropped multiple malicious payloads onto the victim machine, including versions of Lumma Stealer and NetSupport Client RMM.
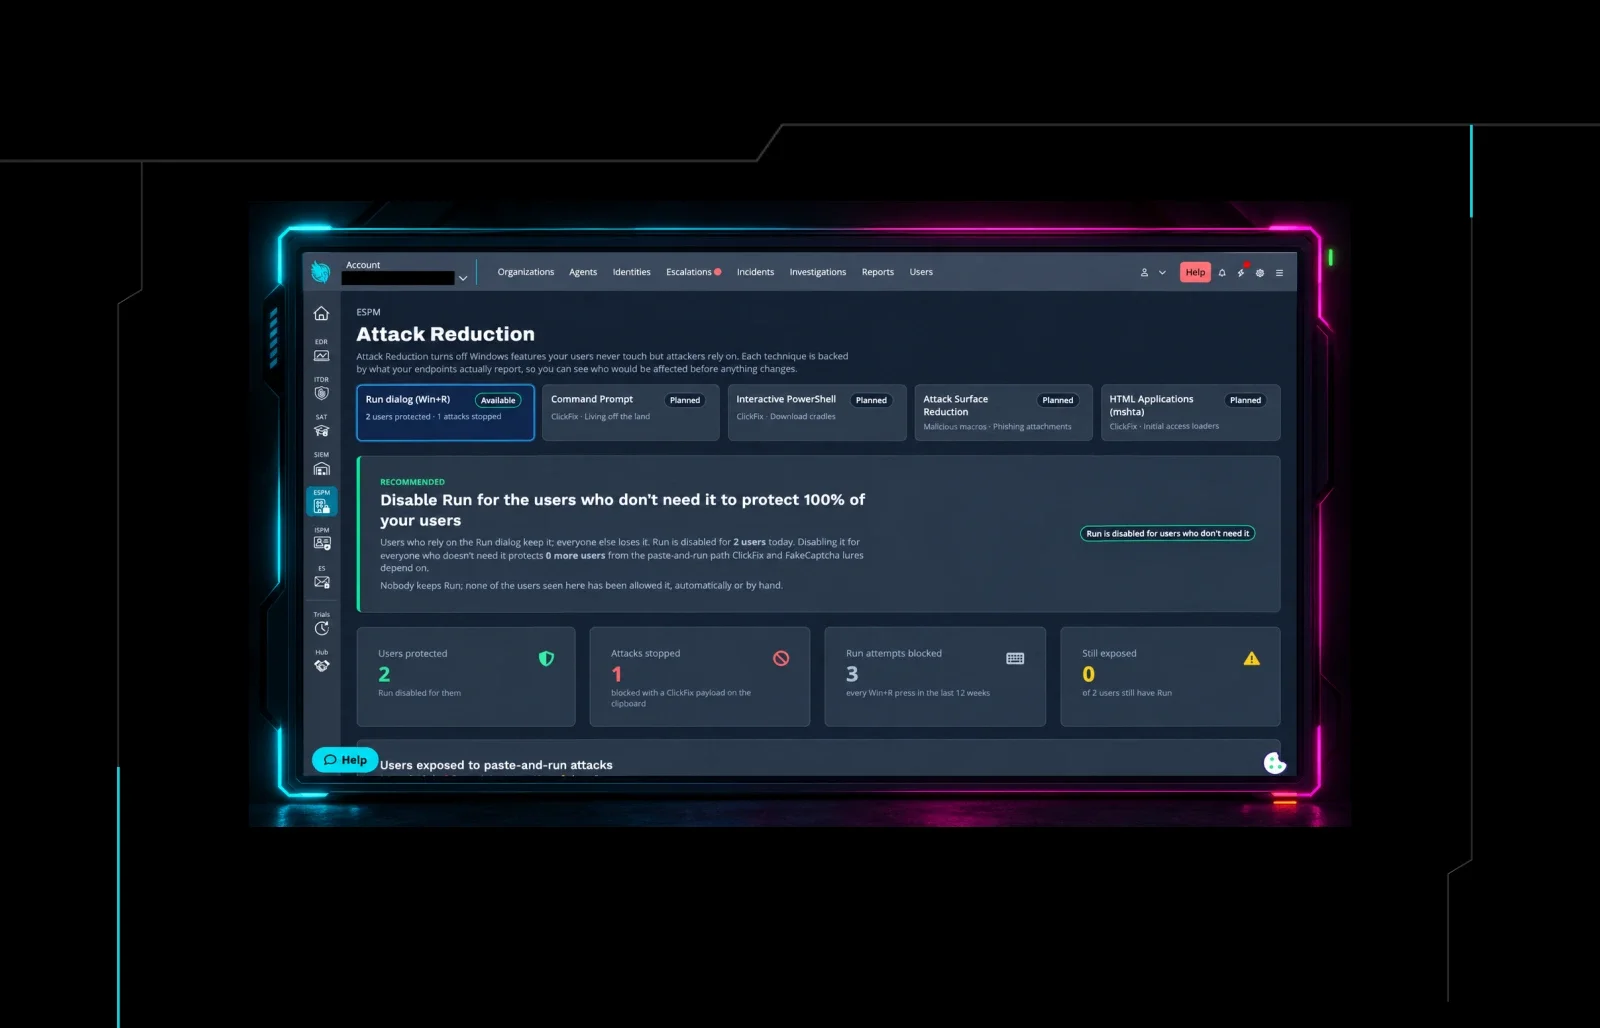
ClickFix tricks users into pasting malicious commands into the Windows Run dialog. See how Attack Reduction in Huntress ESPM helps prevent that from happening.
Attackers may be in your tenant before you connect it. Huntress Managed ITDR Lookback reviews 180 days of Microsoft 365 logins & our SOC acts on active incidents.
Build identity resilience with Identity Posture Assessment, an on-demand Microsoft 365 report that scores your identity defenses and shows how fast you can fix the gaps.
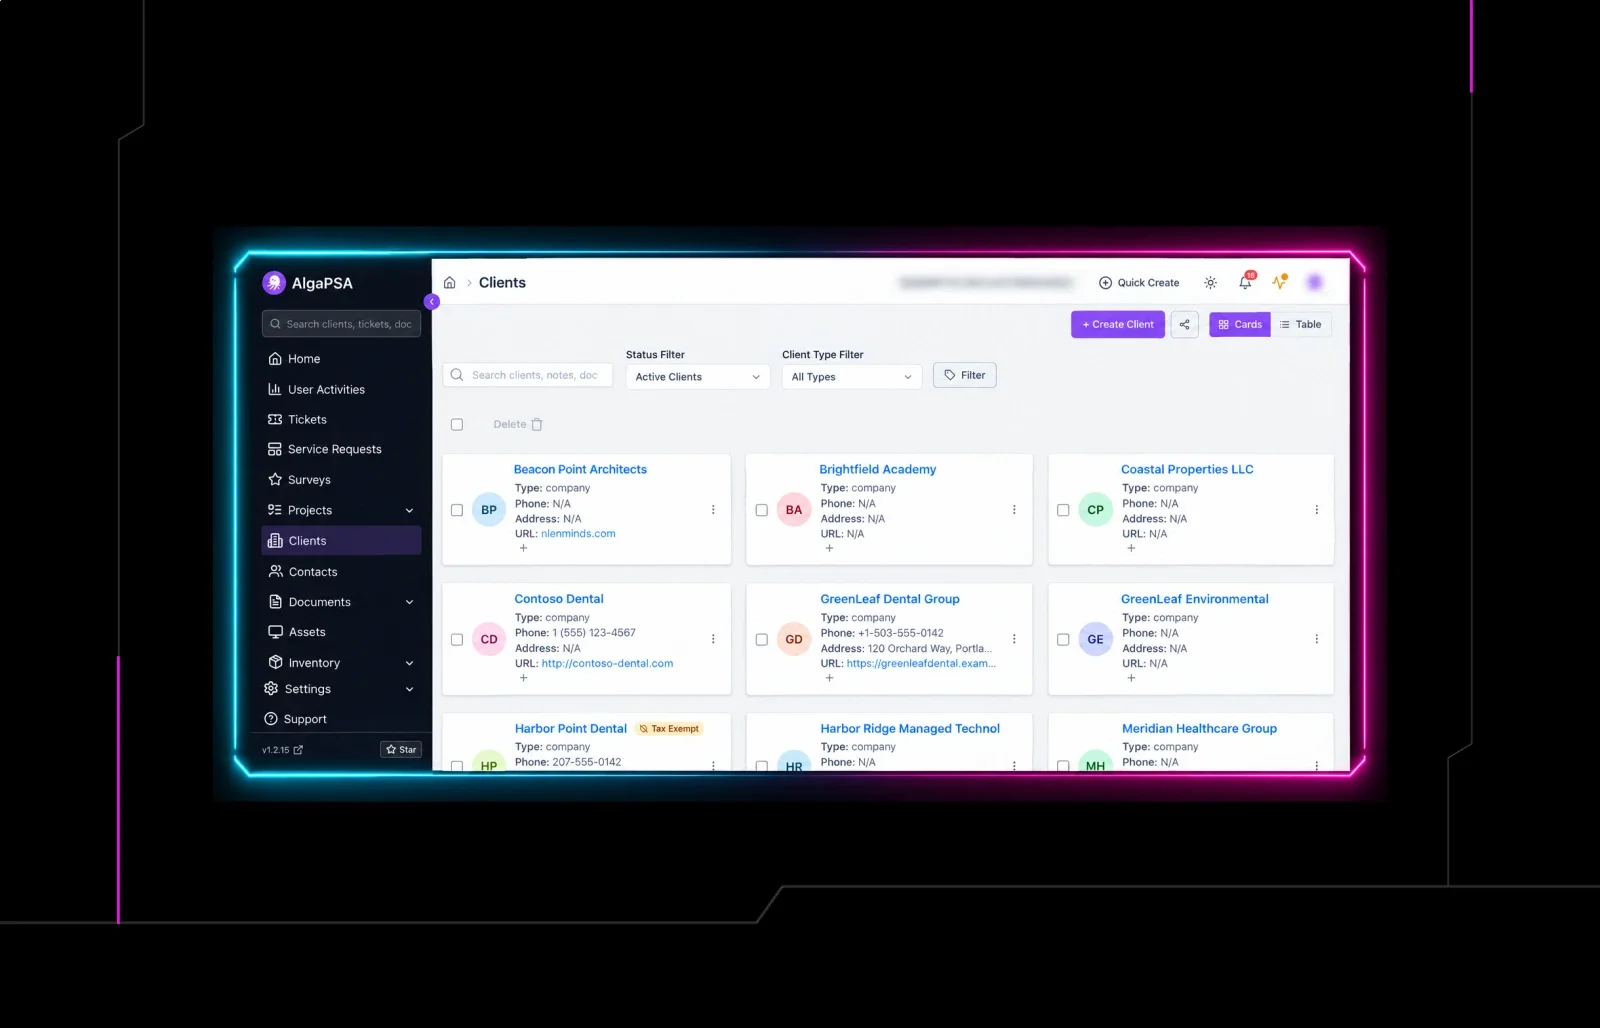
Nine Minds used the Huntress API and public docs to turn Huntress incident reports into AlgaPSA tickets in days. See how they did it and what you can build.
Passkeys significantly improve authentication, but attackers still target enrollment, recovery, endpoints, and alternative flows. Discover how to secure the full account lifecycle with a comprehensive identity strategy.
Doris searched for ChatGPT and ended up in a BEC scam. See how ClickFix, a stolen session cookie, and a hidden inbox rule chain into an OH $#!T moment.
Threat actors are exploiting AhsayCBS flaws, including CVE-2026-105133 and CVE-2026-105134, to deploy webshells and XMRig cryptominers. Update to 10.3.4 and restrict access now.
 Login