❌

Normal view

Reimagining the SOC for the agentic era in Microsoft Defender

23 September 2026 at 18:00

The physics of cybersecurity are changing. So must the security operations center (SOC).

Cyberattackers are using agents to automate execution at unprecedented scale. What once required entire teams now requires a single operator and an agent framework.

That shift has exposed a hard truth: security cannot operate at AI speed when protection and operations are built as separate systems. Every handoff, integration, and boundary slows defenders down. Agents inherit that complexity.

For agentic security to work, the industry needs a different model. It needs a modern cyber stack with the breadth to see across the environment and the depth to investigate and act. Security operations and native protection must function as one system. This is the integrated security operations center (ISOC).

Today we are announcing ISOC in Microsoft Defender: a foundation built for agentic security that brings leading solutions for security information and event management (SIEM) and threat protection together. It gives people and agents a shared foundation to see, understand, and act across the environment, without the complexity of operating separate systems.

Built for agentic security

In July 2026, we introduced the end-to-end cyber stack alongside Project Perception, with the focus of delivering the right models, a harness, and specialized agents to help defenders perceive, reason, and act at machine speed. But we are innovating at every layer of the stack, because intelligence and orchestration alone are not enough. Agents depend on the rest of the stack working as one.

They need signals and sensors that provide visibility, context that turns those signals into understanding, and actuators that translate decisions into protection. With ISOC, these layers work in unison, so agents can move beyond isolated tasks and help operate an agentic SOC.

Diagram of an autonomous system stack with six layers: Actuators, Agents, Harness, Models, Context, and Sensors and Signals. The bottom three layers are grouped together. A banner below reads, "Strategy stays human. Scale becomes autonomous."

Signals and sensors give the system awareness.

Context turns those signals into understanding.

Actuators turn insights into protective action.

ISOC brings these capabilities together as a foundation, so humans and agents can operate as one system, each contributing what they do best. Agents provide the speed and scale to execute continuously, while people set priorities, apply judgment, and define the outcomes that matter. Together, they empower defenders to keep pace with AI-powered threat actors and achieve better security outcomes.

Integrated protection loop

With ISOC enabling signals, context, and controls to work as one, it breaks the pattern of linear security workflows. The result is an integrated protection loop that continuously turns what defenders learn into stronger pre-breach protection.

Attack disruption in Microsoft Defender shows what this makes possible. Rich telemetry and controls enable the system to detect, predict, and adapt to an attacker while the attack is still unfolding. It disrupts threats in progress and anticipates where attackers may move next. It’s a protection loop that uses exposure insights to strengthen protection in near real-time with threat intelligence focusing the loop on the threats that matter most.

ISOC brings together the capabilities needed to make this loop native, eliminating the burden of assembling, tuning, and maintaining it yourself. And as protection advances, new capabilities can become part of that loop. The result is stronger protection and a different way of working, where practitioners spend less time chasing individual signals and more time applying judgment, setting priorities, and driving security outcomes.

Designed for the practitioner

For too long, practitioners have had to compensate for the boundaries in their security architecture, stitching together signals, rebuilding context, and moving between tools just to get the information and controls needed to act.

ISOC changes their starting point. The capabilities practitioners need to investigate, hunt, automate, manage incidents, understand threats, and take action are brought together and available by default. Instead of organizing their work around the boundaries between tools, teams can organize around the security outcome they are trying to achieve.

And that foundation gets more powerful as autonomy grows. The integrated protection loop can take on more of the continuous work of detecting and defending against threats, while agents help practitioners investigate, reason, and act using the same context and controls already available to them.

There’s no separate agentic layer to assemble or new operating model to stitch together. Practitioners can multiply their expertise where they already work, shifting more of their time from operating the security stack to directing the defense.

The path forward

Security has always been a race between attackers and defenders. AI changes the speed, scale, and economics of that race. The next SOC will not be defined by how many AI features it has, but by whether people and agents can perceive, reason, and act across an environment as one system.

Integrated security operations center (ISOC) in Microsoft Defender is available in preview today. Watch a recording of the full announcement or download the whitepaper: Agentic SOC: The new operating model for continuous defense.

To learn more about Microsoft Security solutions, visit ourβ€―website.β€―Bookmark theβ€―Security blogβ€―to keep up with our expert coverage on security matters. Also, follow us on LinkedIn (Microsoft Security) and X (@MSFTSecurity)β€―for the latest news and updates on cybersecurity.

The post Reimagining the SOC for the agentic era in Microsoft Defender appeared first on Microsoft Security Blog.
Improving email security outcomes with real-world Microsoft Defender insights

17 September 2026 at 18:00

Every benchmark tells a story. The most valuable ones tell us where to improve next.

For five consecutive quarters Microsoft has published email security benchmarking reports to provide greater transparency into real-world protection outcomes. The results have shown strong Microsoft Defender performance across pre-delivery and post-delivery scenarios, while revealing where threats and defenses continue to evolve.

This quarter’s benchmark examines how continuous measurement informs protection across prevention, detection, and adaptation, and how those insights are helping improve customer outcomes.

Key takeaways

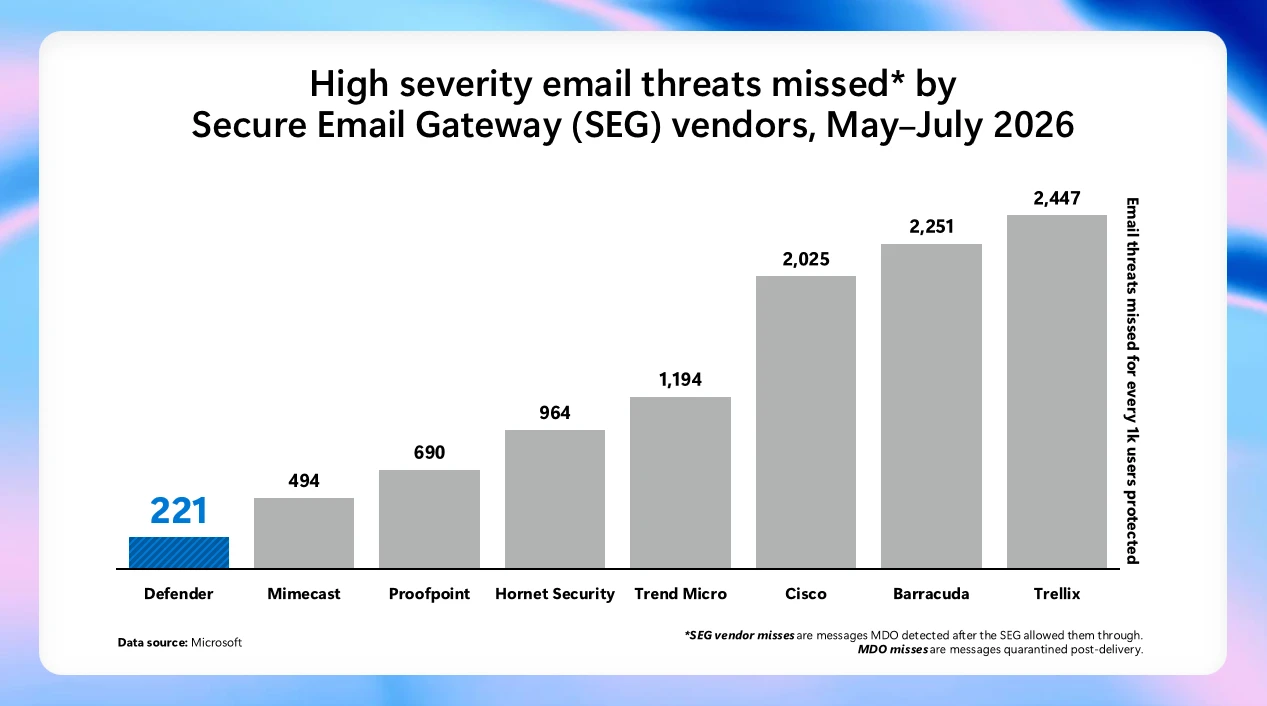
  • Defender again missed the fewest high-severity threats among the solutions evaluated, about 55% fewer than the next-closest secure email gateway (SEG) vendor.
  • Layered security adds the most value in promotional and bulk filtering and works; gains for spam and malicious email remain comparatively modest.

Benchmarking results for SEG vendors

In the latest quarterly SEG comparison from May 2026 through July 2026, Defender missed 221 high-severity threats per 1,000 protected users, 55.4% fewer than the next-closest SEG vendor. The benchmark measures missed threats instead of the total number of malicious emails that were caught and filtered, because catch totals can reflect differences in threat volume and exposure across vendor environments. By normalizing missed threats per 1,000 users we are able to provide a more consistent side-by-side comparison.

The image shows a bar chart illustrating the number of high severity email threats that were missed by various Secure Email Gateway (SEG) vendors, with Mimecast leading the list.
Figure 1: High-severity email threats missed by SEG vendors (May 2026 through July 2026), measured as threats missed per 1,000 users protected. Data source: Microsoft Defender.

If you’ve read our previous blogs, you’ll see that missed threats have increased across multiple reporting periods, including for Microsoft. This aligns with broader trends we’re seeing as AI makes it easier for cyberattackers to gather public information, tailor messages, and create more convincing impersonation attempts. It reinforces the need for protection that continuously adapts.

Benchmarking results for ICES vendors

Effective email detection combines pre-delivery filtering with post-delivery detection and remediation. This benchmark helps customers evaluate where each layer contributes measurable value.

Similarly to previous quarters, integrated cloud email security (ICES) solutions continue adding the most value in promotional and bulk filtering. We saw an improvement in ICES vendor malicious catch at 0.30% versus 0.13% in the last quarter and spam catch going up to 0.52% versus 0.28% compared to last quarter.

The diagram illustrates the distribution of different types of cyber threat catches (non-malicious, spam, and malicious) detected by various vendors (Check Point, Cisco, Darktrace, etc.) in Microsoft Defender Counter Attack (ICES) from May to July 2026.
Figure 2: ICES vendor catch contribution (May 2026 through July 2026). Data source: Microsoft Defender.

Defender caught 92% of post-delivery malicious messages on average during the benchmark period, highlighting how the combination of pre-delivery and post-delivery remediation delivers strong results for customers.

At the same time it’s key to understand that Defender doesn’t treat post-delivery remediation as a point-in-time action after the email was first delivered to the inbox. Even after a message reaches the inbox, new threat intelligence can reveal risks that were not apparent at the time of delivery. Defender continuously reevaluates delivered messages and remediates threats as new indicators, campaign intelligence, and threat signals emerge.

The image is a pie chart showing the percentage of malicious emails detected by various security vendors, with Microsoft Defender catching the most at 92%.
Figure 3: Post‑delivery malicious catch by Microsoft Defender (May 2026 through July 2026), shown across vendors and overall average. Data source: Microsoft Defender.

How our benchmarking is helping shape product innovation

The value of benchmarking is what happens after measurement. Insights from customer feedback, threat telemetry, and benchmarking have informed recent Microsoft Defender investments:

  • More control over promotional mail: Across multiple benchmarking periods, we observed that ICES solutions often delivered the greatest incremental benefit in filtering promotional and bulk email. The new Promotions folder in Outlook builds on these insights by helping users reduce inbox clutter while keeping legitimate marketing and bulk messages accessible.
  • Redesigned machine learning and AI model stack: By analyzing and incorporating natural language processing signals, including message topic, alongside other AI detection signals, Defender can improve detection accuracy. During a consecutive four-week period, Microsoft research observed a roughly two-thirds reduction in false negatives and a nearly one-fifth reduction in false positives for Defender customers.
  • Protection for people and AI: We built prompt injection protection to detect and isolate malicious AI instructions in email before deliveryβ€”helping protect not only people, but also Copilot, agents, and other AI systems that read and act on inbox content. This innovation demonstrates how we continue evolving our defenses to address the latest cyberattack techniques and stay ahead of emerging threats.

Looking ahead

Since July 2025, our goal has been to bring greater transparency to email security effectiveness. Today, we are using benchmarking to help customers understand how cyberthreats evolve, where defenses add value, and how protection improves over time.

Benchmarking is not simply about demonstrating effectiveness, it is about learning from real-world outcomes and translating those insights into stronger protection. As cyberattackers continue to innovate, we remain committed to sharing evidence, improving our technology, and helping customers stay ahead of emerging cyberthreats.

To explore the latest benchmarking data and learn more about how Defender and ICES partners work together, access the benchmarking site.

Learn more

Learn more about Microsoft Defender.

To learn more about Microsoft Security solutions, visit our website. Bookmark the Security blog to keep up with our expert coverage on security matters. Also, follow us on LinkedIn (Microsoft Security) and X (@MSFTSecurity) for the latest news and updates on cybersecurity.

The post Improving email security outcomes with real-world Microsoft Defender insights appeared first on Microsoft Security Blog.

❌