❌

Normal view

GTA 6 before release: fake leaks, β€œearly access”, and other scams | Kaspersky official blog

Gamers around the world are holding their breath for November 19, 2026, the day Grand Theft Auto VI is expected to drop. Many of them have been waiting for the next installment in the hit series for over a decade. For die-hard fans, the final months before launch could prove especially agonizing. Sadly, scammers know all about this hotly anticipated release too, and they’ve decided to use it as a lure to launch all sorts of attacks on gamers. We’ve spotted a great many bait sites aimed at impatient GTA VI fans. Today, we walk you through exactly how these crooks try to trick gamers, and how you can avoid becoming their next target.

1. β€œGTA VI has already leaked, and all you have to do is pay”

One site our experts found, called CyberLeek, claims to have an early build of GTA VI, and pretends to offer three different ways to get hold of the game before its official release. The first and priciest option is to buy the β€œfull game” of GTA VI for US$1000. For that price, buyers are offered an early build of the game, exclusive content, and a direct download link. This is claimed to be a limited offer: only one copy per customer.
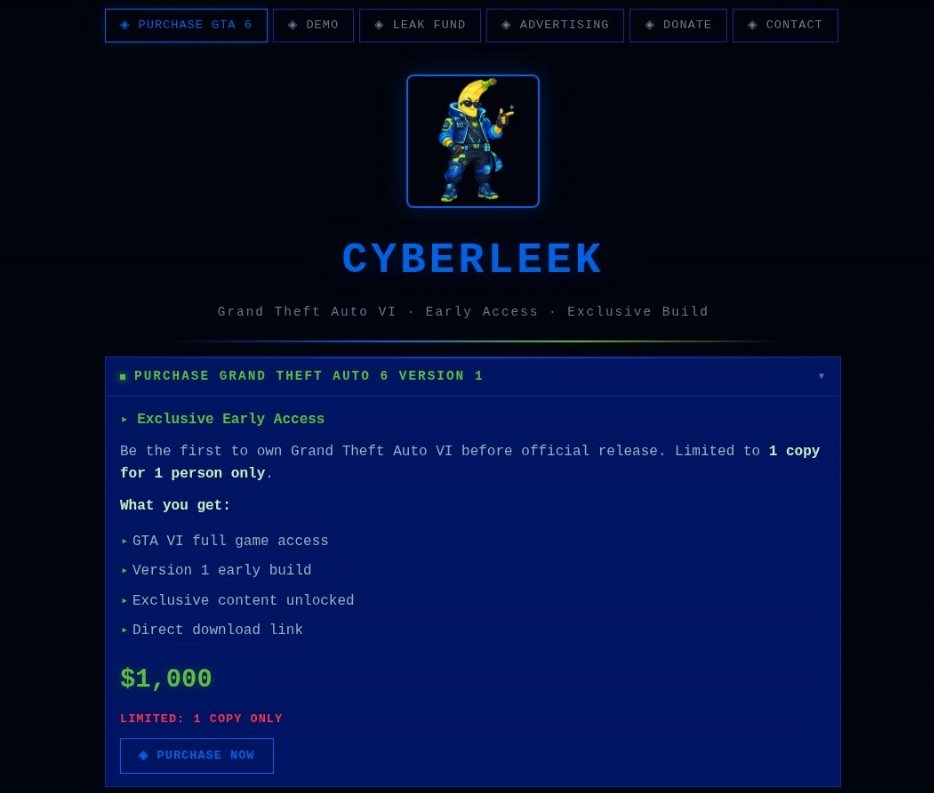
CyberLeek offers buyers a full early build of the game, exclusive content, and a direct download link

An alleged GTA VI leak advertised for US$1000

For those not ready to part with a thousand dollars, there’s a cheaper option: for a hundred dollars, users can get 24-hour access to the GTA VI demo.

Finally, the third option relies on crowdfunding. Playing modern-day Robin Hoods, the site’s creators claim they’ll raise $50,000 and then release the game to the public for free, with everyone who donates at least $100 getting priority early access. But dig into the fine print, and the fundraising goal for that paid early access suddenly jumps from $50,000 to $500,000. Looks like one of the scammers sat on their keyboard hit an extra zero by accident.
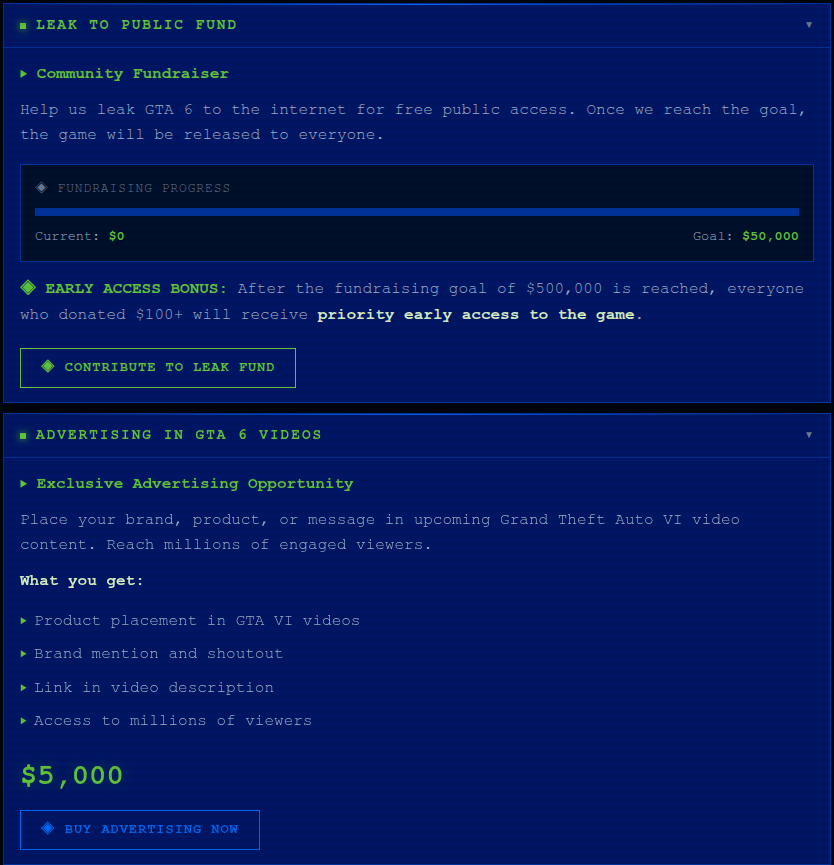
Raising money to release GTA VI

An urgent fundraiser for US$50,000 β€” or is it US$500,000? β€” to release a leaked GTA VI build, plus advertising opportunities for businesses

But CyberLeek’s lineup of tempting β€œoffers” doesn’t stop there; there are also services for businesses. For US$5000, the site’s creators offer to place an ad right inside Grand Theft Auto VI: a logo, a product, or a brand mention that will supposedly show up in some unspecified β€œupcoming Grand Theft Auto video content”. What exactly that means is unclear: in-game clips or cutscenes, trailers, or just some gameplay footage. And honestly, the price seems suspiciously low for product placement in one of the most anticipated games in recent years.

This offer looks especially amusing next to the supposedly complete early build of the game with full access available on the same website. So, apparently, the game is already finished enough to sell in full, but you can still somehow slap ads into it.

One can only pay for all these incredible services with cryptocurrency. CyberLeek accepts Bitcoin, Ethereum, USDT, and Litecoin, and the site’s creators make a point of saying that all payments are final and no refunds are possible. Well, we weren’t expecting refunds anyway.

That said, this is just one example. CyberLeek started out as the nickname of the hacker behind both the recent Rockstar Games breach and GTA VI content leak. Later on, other cybercriminals began using that same name to build a whole bunch of fake sites. Despite having completely different designs, all of these sites attempt to project an association with CyberLeek, enticing users with (false) promises of access to β€œofficial” leaked versions of GTA VI. Whichever of these sites you come across, we’d strongly advise against using your own computer to check what’s actually hiding inside the archives and installers they hand out.
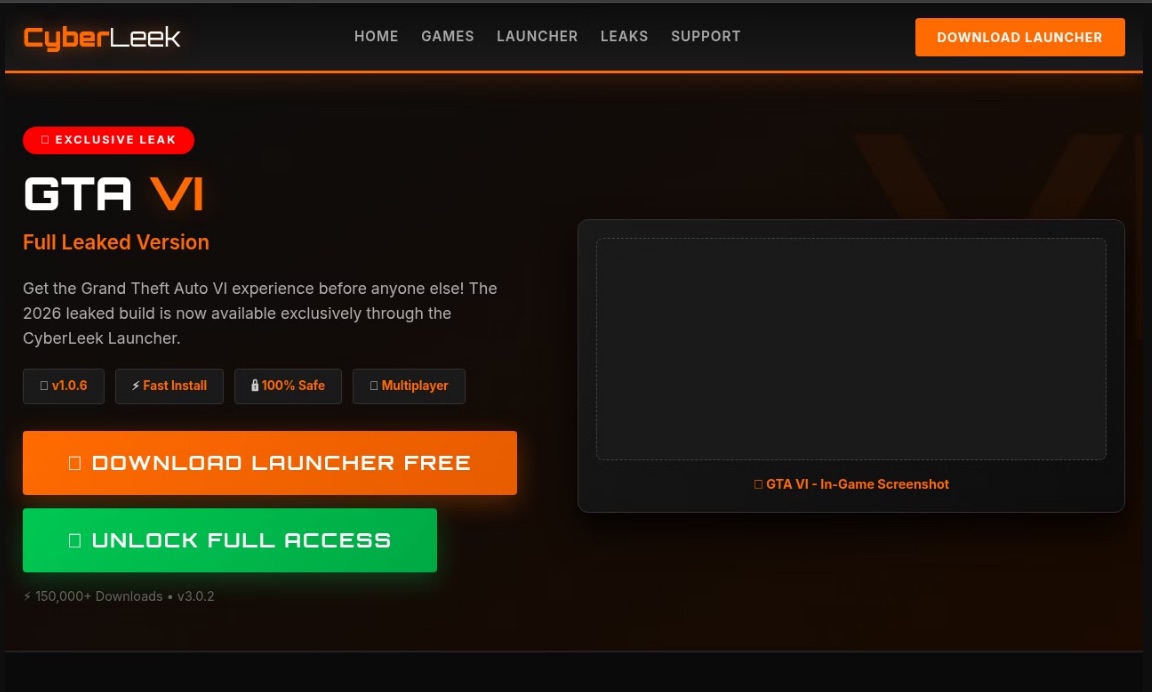
Yet another CyberLeek site advertising an

Another CyberLeek site offering access to a β€œleaked build” of GTA VI invites the user to download some unknown launcher, or β€œunlock” the full version of the game β€” whatever that means

2. Preordering Grand Theft Auto VI β€” with a catch

This bait targets slightly more sensible gamers β€” the kind who aren’t trying to download GTA VI right this second but wouldn’t say no to grabbing a free preorder code ahead of time. Our experts found a site that is claiming to hand out a redeem code for the PlayStation 5 or Xbox Series X|S. All one needs do is pick a platform and provide an email address.

To make it all look convincing, the site even shows off its own β€œstatistics”: it supposedly has 3480 active users, and only 121 codes are still available as of today.
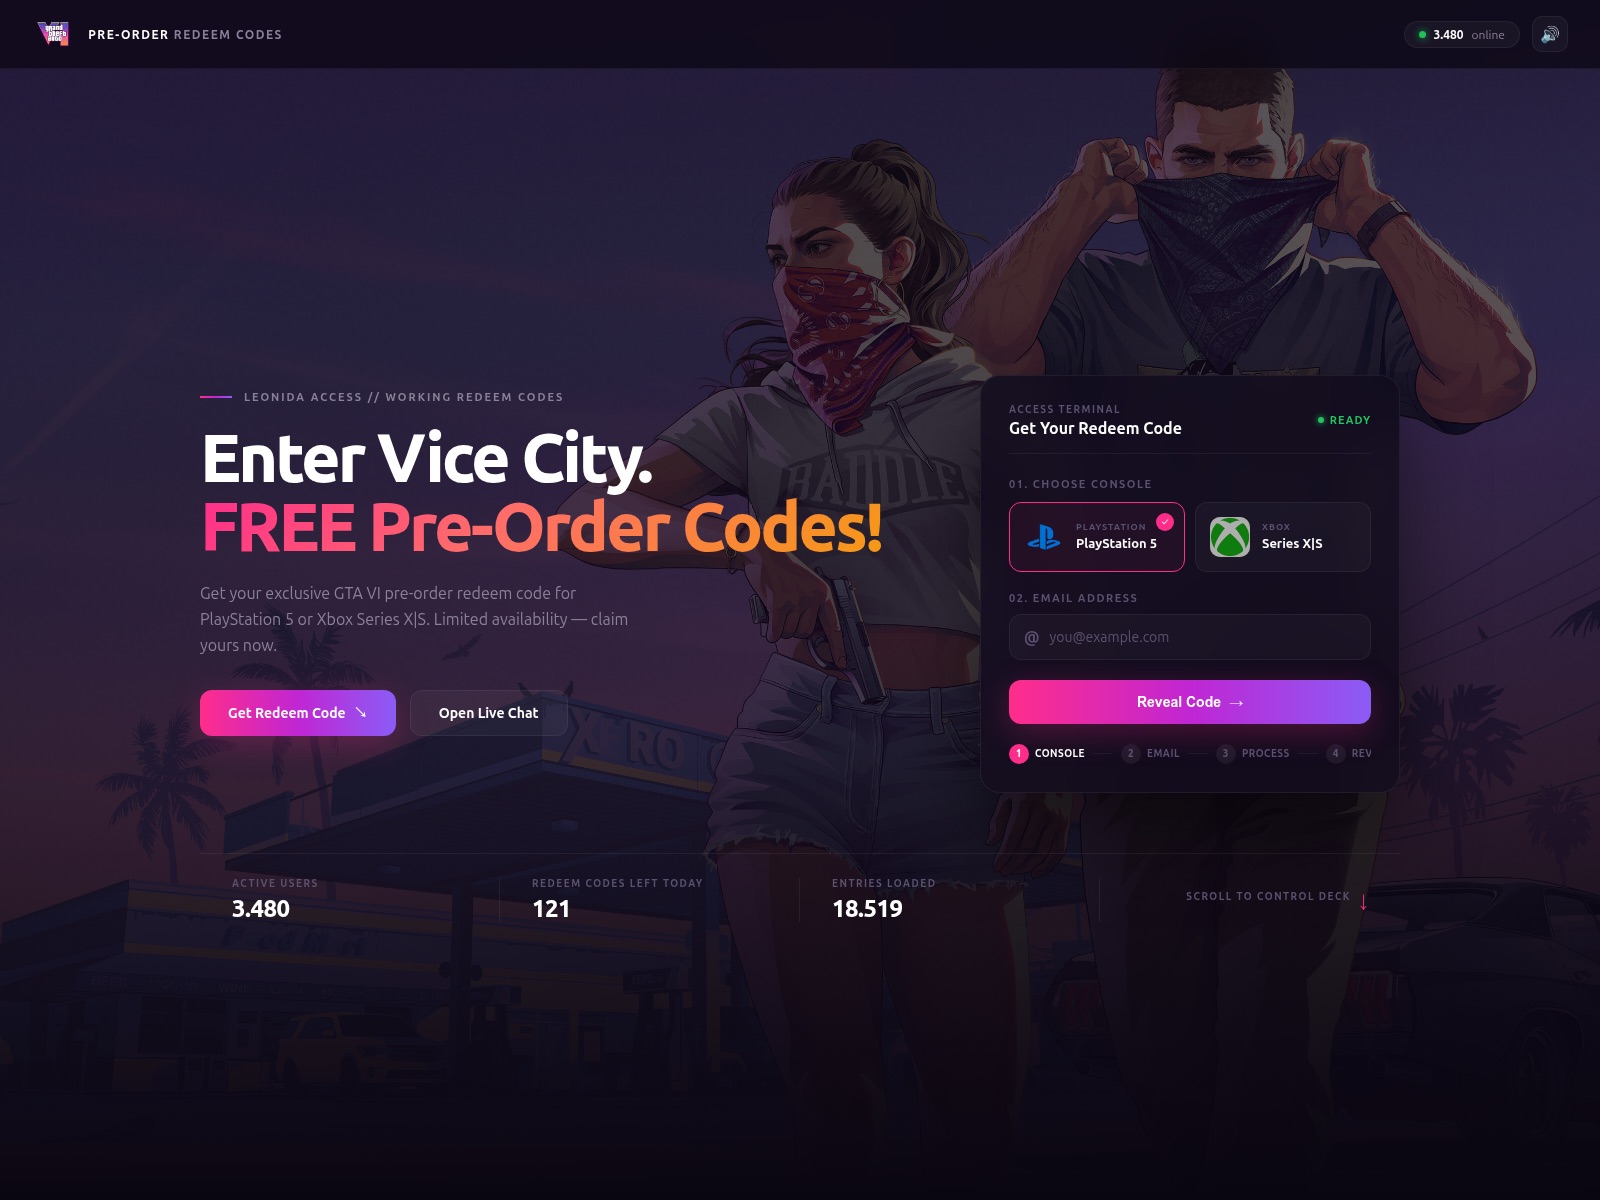
Free GTA VI preorder codes

To get the β€œexclusive code”, the user is asked to pick a console and provide their email address

After picking a console, entering an email address, and clicking Reveal Code, the user lands on a new page. It shows the first four characters of a supposedly generated code, and to get the rest the user is asked to complete an additional check. They’re given 15 minutes to do so.
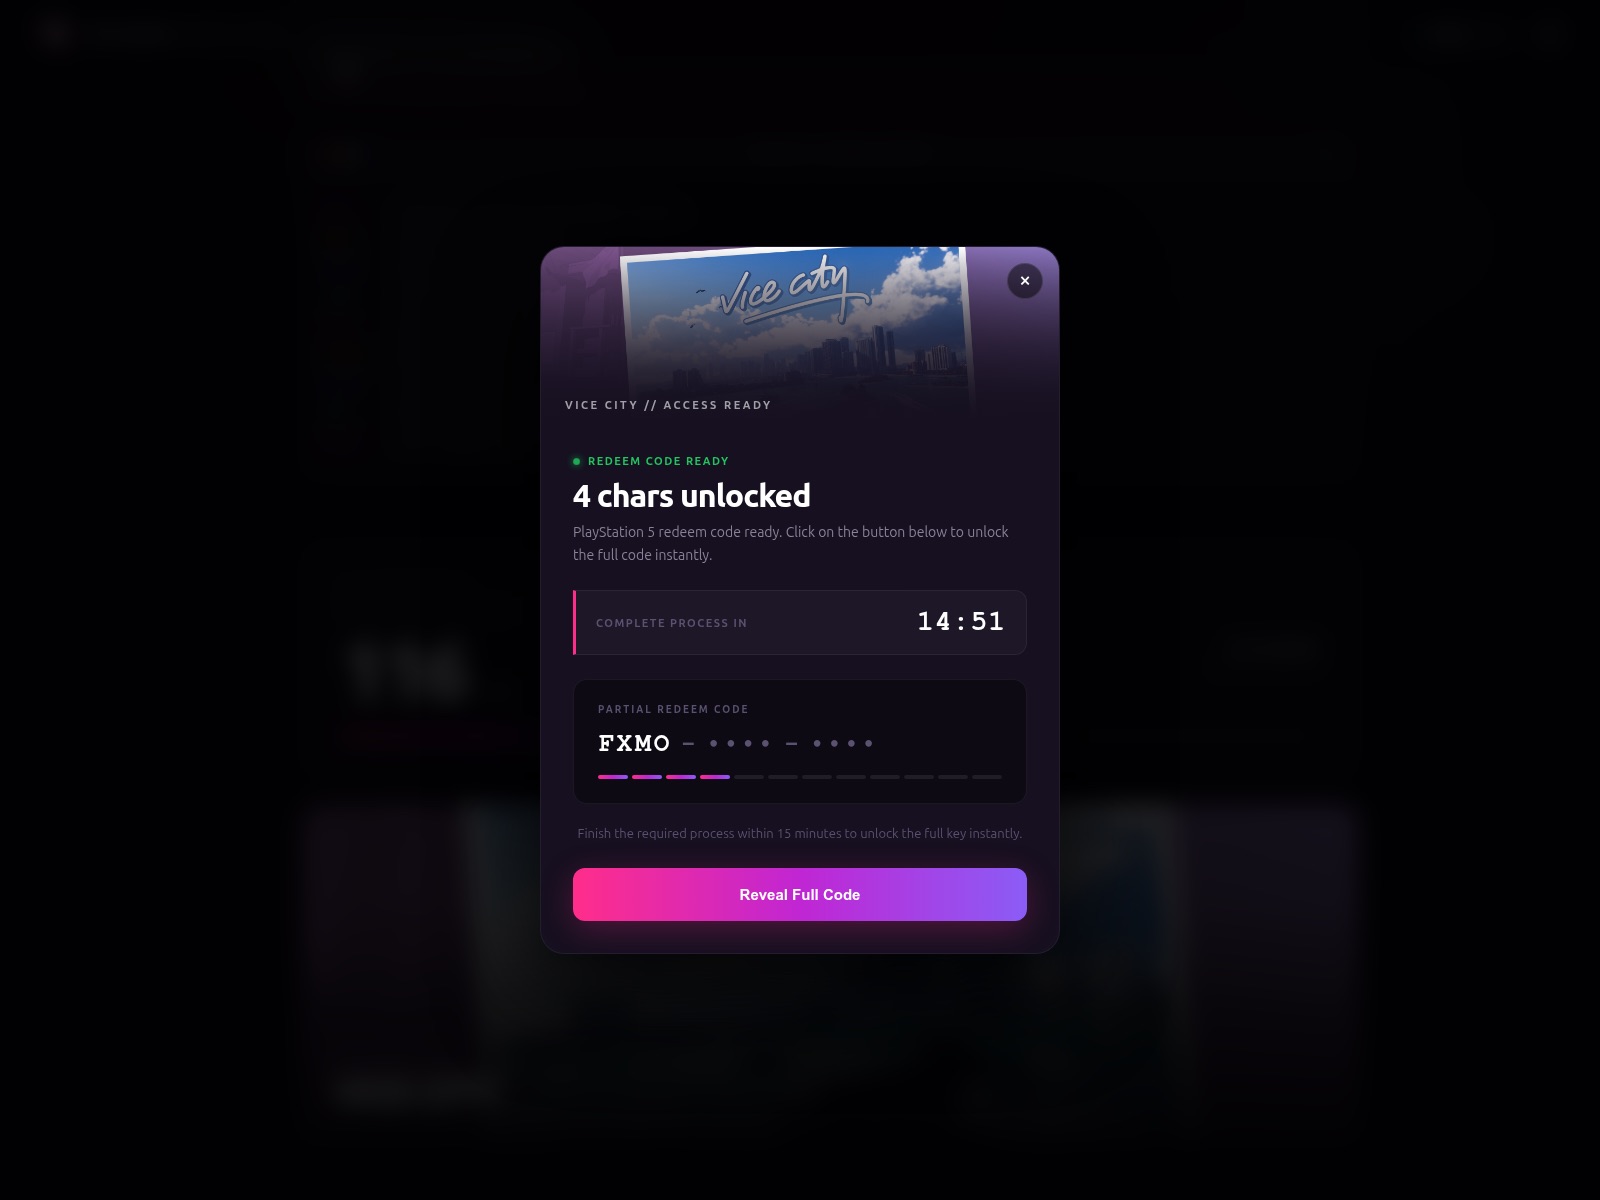
Four characters from the promised code

The site shows the first four characters of the coveted code, and promises to send the rest after an additional check, which the user has 15 minutes to complete

Nobody tells the gamer upfront what this check actually involves. But the next page, which opens after clicking Reveal Full Code, inexplicably turns out to be in German. Here, the user is asked to pass a β€œhuman verification”: download a free AI chat app for their computer, run it, and accept the terms of use.

The real point of this β€œverification” most likely boils down to driving traffic to third-party, often shady, or outright fraudulent sites, with GTA VI simply used as bait to pump up visitor numbers.
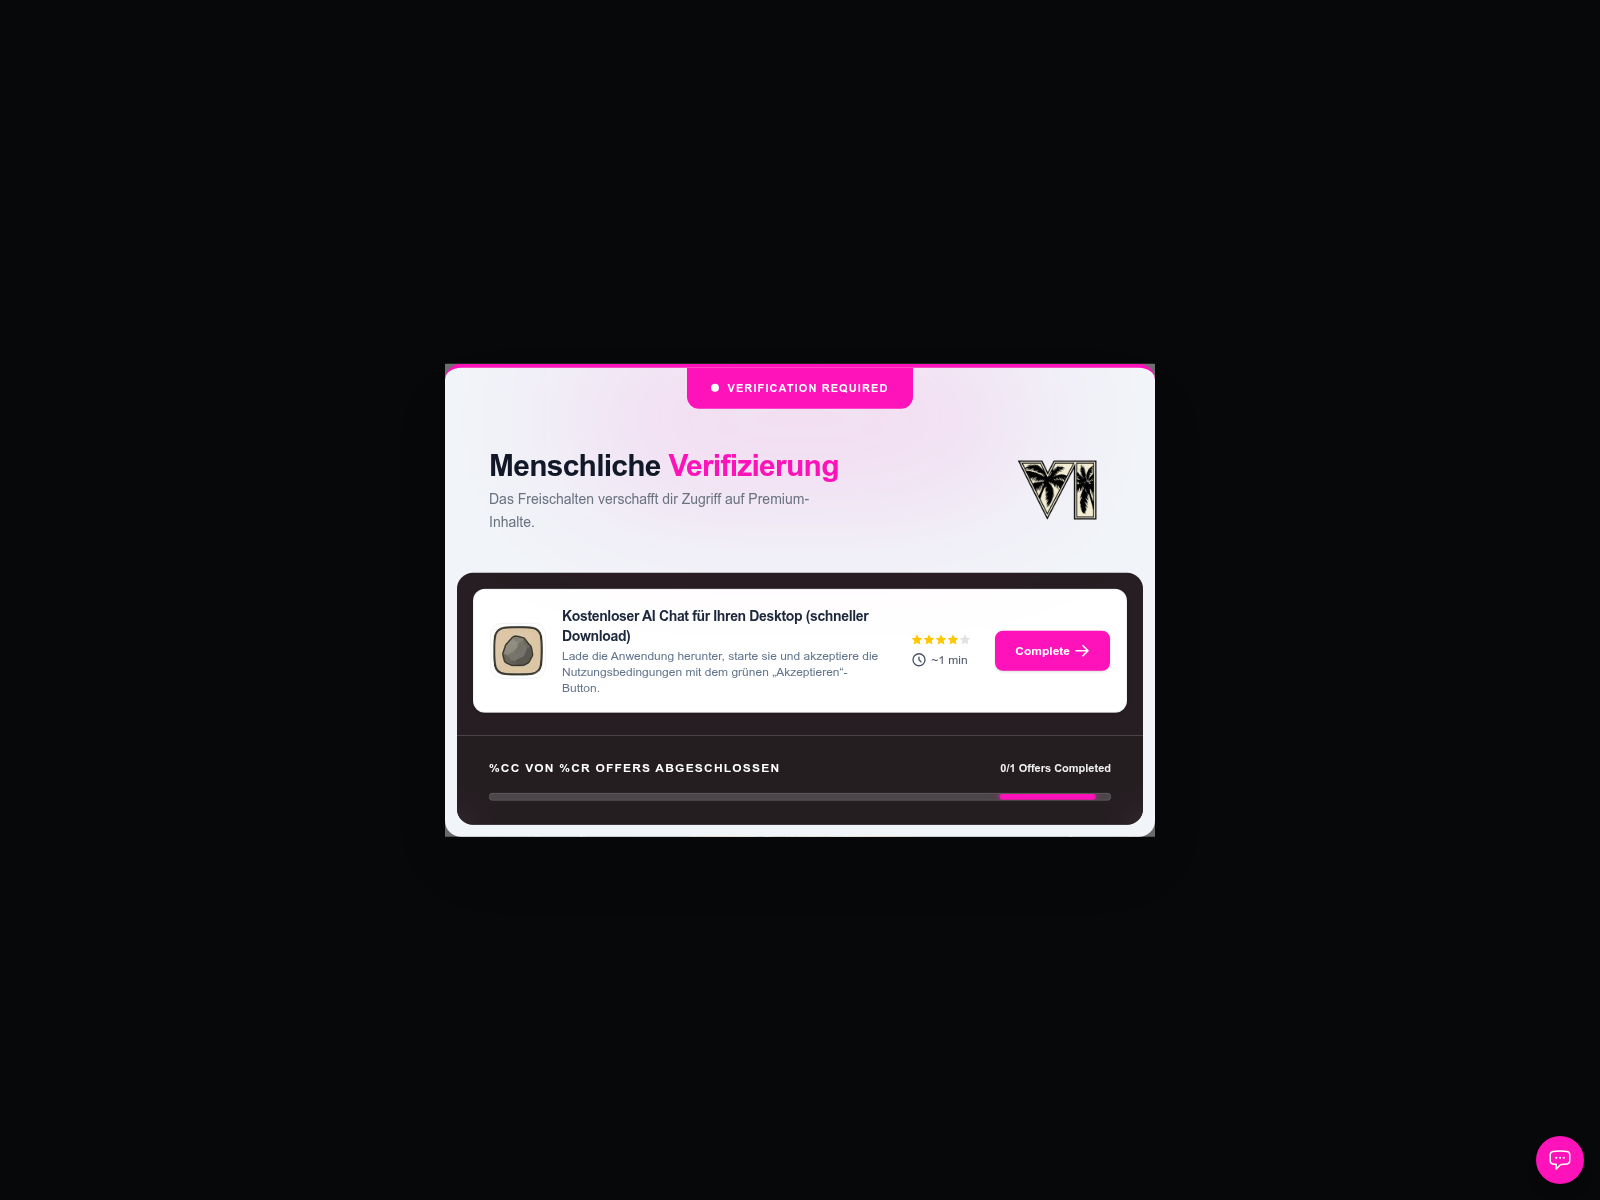
Unknown app instead of a GTA VI code

To get the rest of the β€œcode”, the site demands that the user download and run an AI chat app and accept its terms of use

A simpler variation involves fake sites that simply collect money under the pretext of placing preorders for Grand Theft Auto VI. For example, a fake PlayStation Store site targeting Brazilian users offers preorders for R$449.9, which actually matches the official price in the real PS Store. The user can pay with a credit card or through Pix (Brazil’s instant payment system), but along with their money, they’d also have to hand over personal data, including their CPF β€” the Brazilian equivalent of a taxpayer identification number.
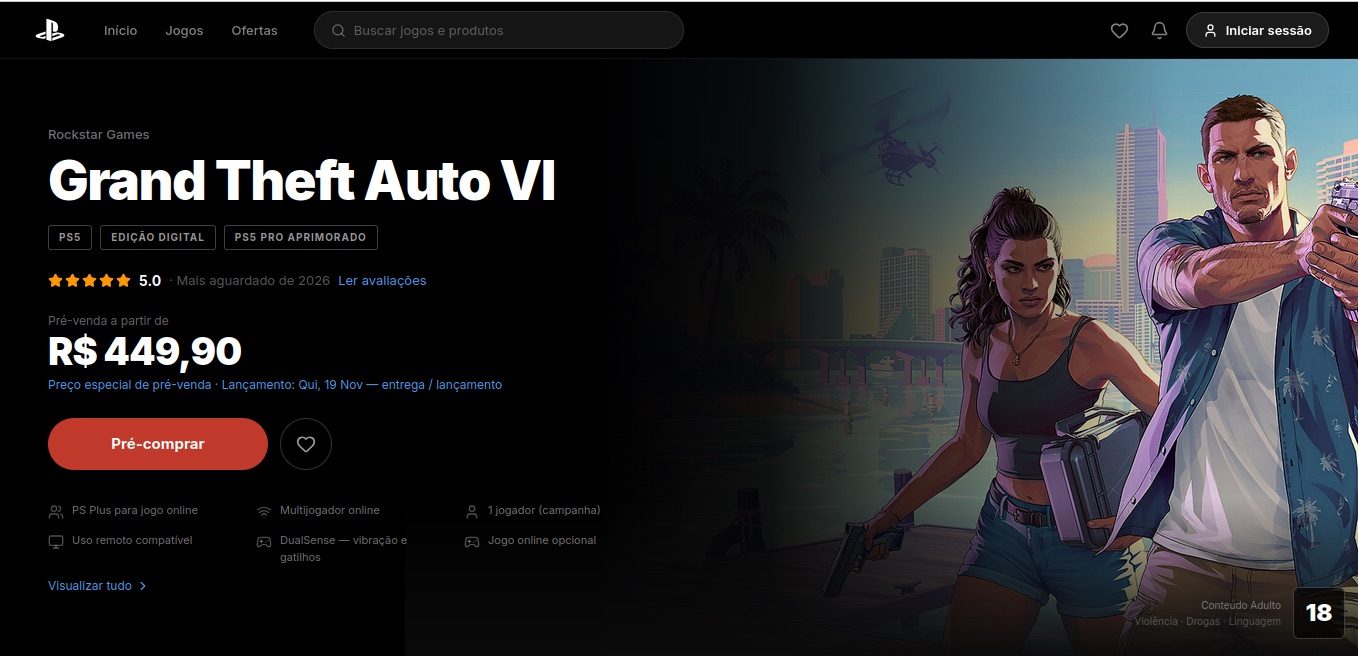
Fake GTA VI preorder at the official price

In Brazil, a fake PlayStation Store site collects money for GTA VI preorders at a price that looks legit

3. You’ve missed it: GTA VI is already out!

Some scammers don’t even bother with elaborate stories about leaks, beta tests, or preorder deals. They simply build websites that copy the look and feel of GTA, and invite users to start playing GTA VI right here, right now. We came across a few examples of these sites.
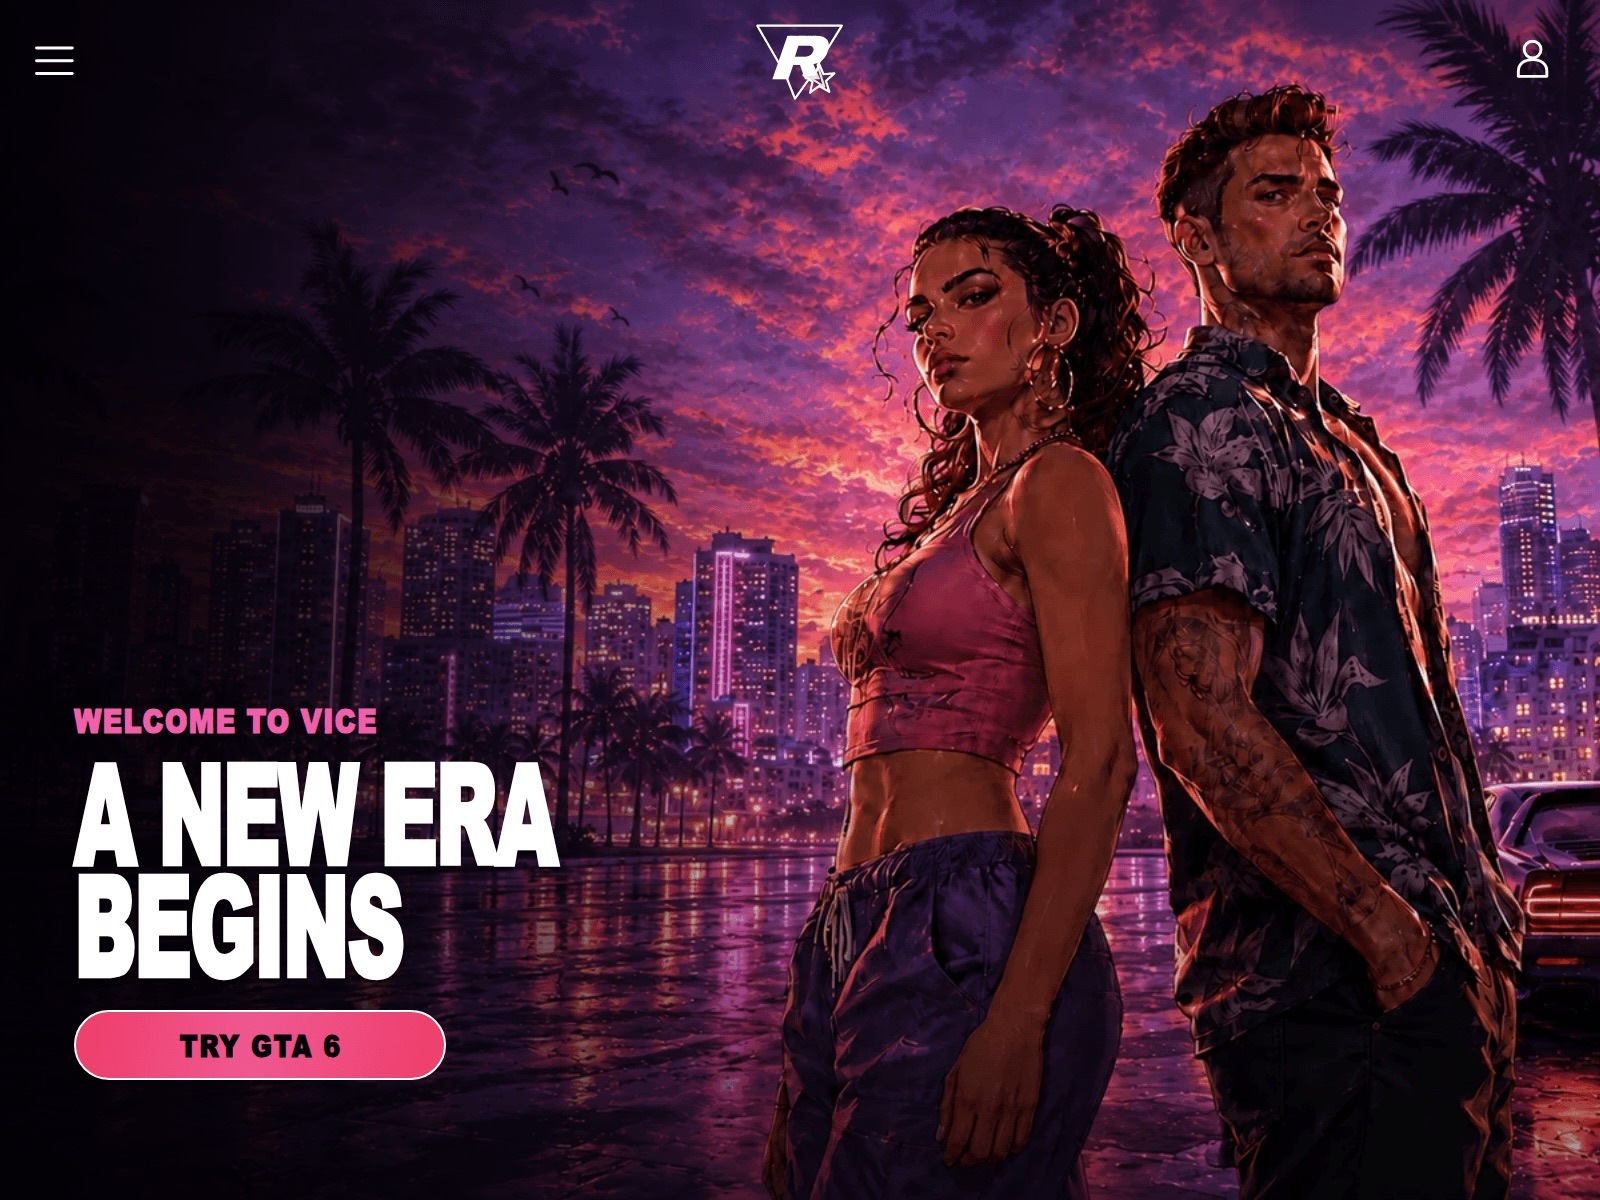
GTA VI β€” right here, right now

No leaks, no tests, no codes needed: visitors are simply invited to click Try GTA 6 and start playing

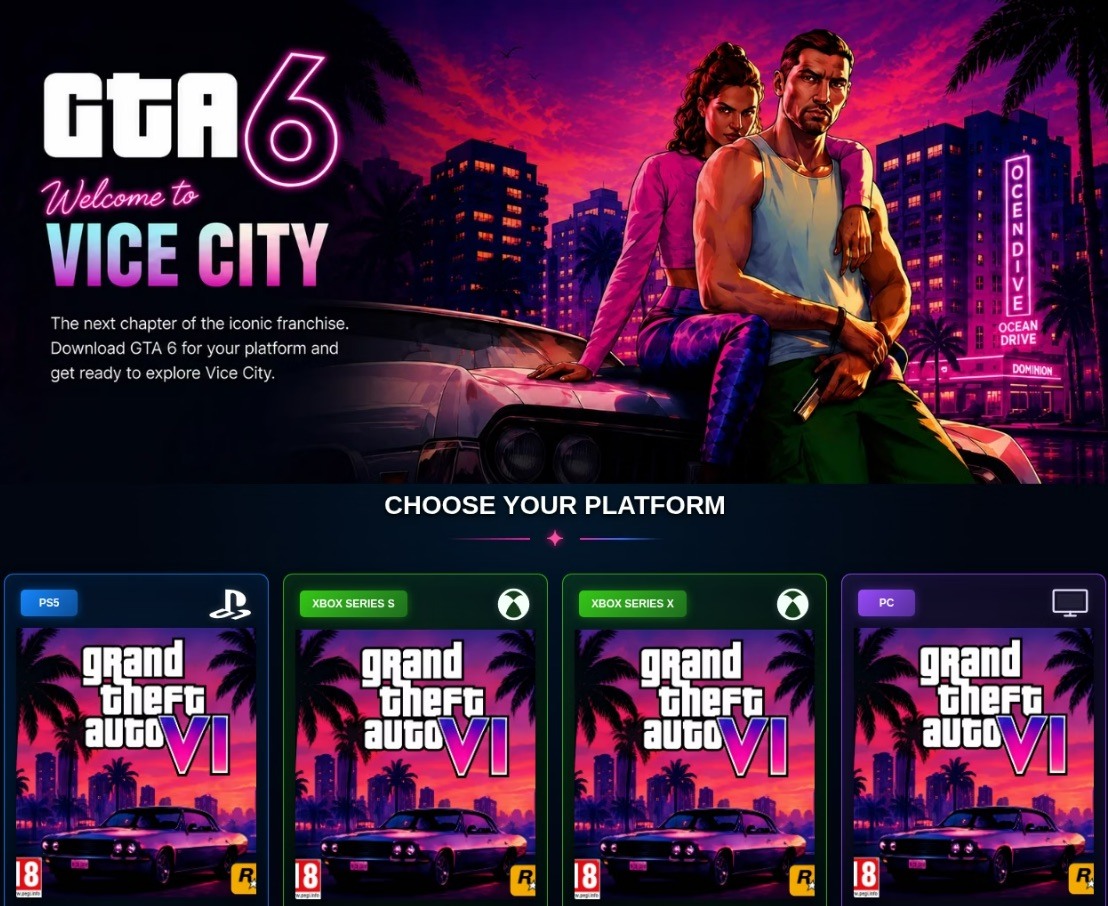
One of these sites tells users they can download GTA VI, as long as they first pick their platform. The range of options is surprisingly generous: a PC version as well as versions for PlayStationΒ 5 and Xbox Series X|S.

GTA VI on any platform

Users are invited to pick a version of GTA VI for PlayStation 5, Xbox Series X|S, or PC

Just to be clear, GTA VI’s official release is still more than a month away, so there’s no way one can download and install the game right now. Nobody knows exactly what users would be getting on their devices instead of the game if they download from one of these sites, but it’s definitely nothing useful. And no matter how carefully scammers copy GTA’s signature style and slap on the Rockstar logo, the address bar usually gives the game away: check the domain and compare it with the official Rockstar Games website address.

4. The icing on the cake: GTA VI for tokens

And finally, what would 2026 be without cryptocurrency? We found a site whose creators were probably inspired by the CyberLeek story and decided to ride the wave of GTA VI’s popularity to promote a token with the refreshingly straightforward name $GTAVI. The whole site is styled after GTA VI and Vice City.

The creators of the project have gone out of their way to highlight the perks of holding the token. They call $GTAVI β€œthe only GTA VI coin that actually rewards its holders”. Whatever the meaning of that tagline, the project’s declared ultimate goal sounds even more tempting: every token holder will get access to Grand Theft Auto VI just by virtue of owning $GTAVI. Think about that for a second: it’s not exactly a direct promise of a free copy of GTA VI, but more like an aspiration on the part of the crypto developers.
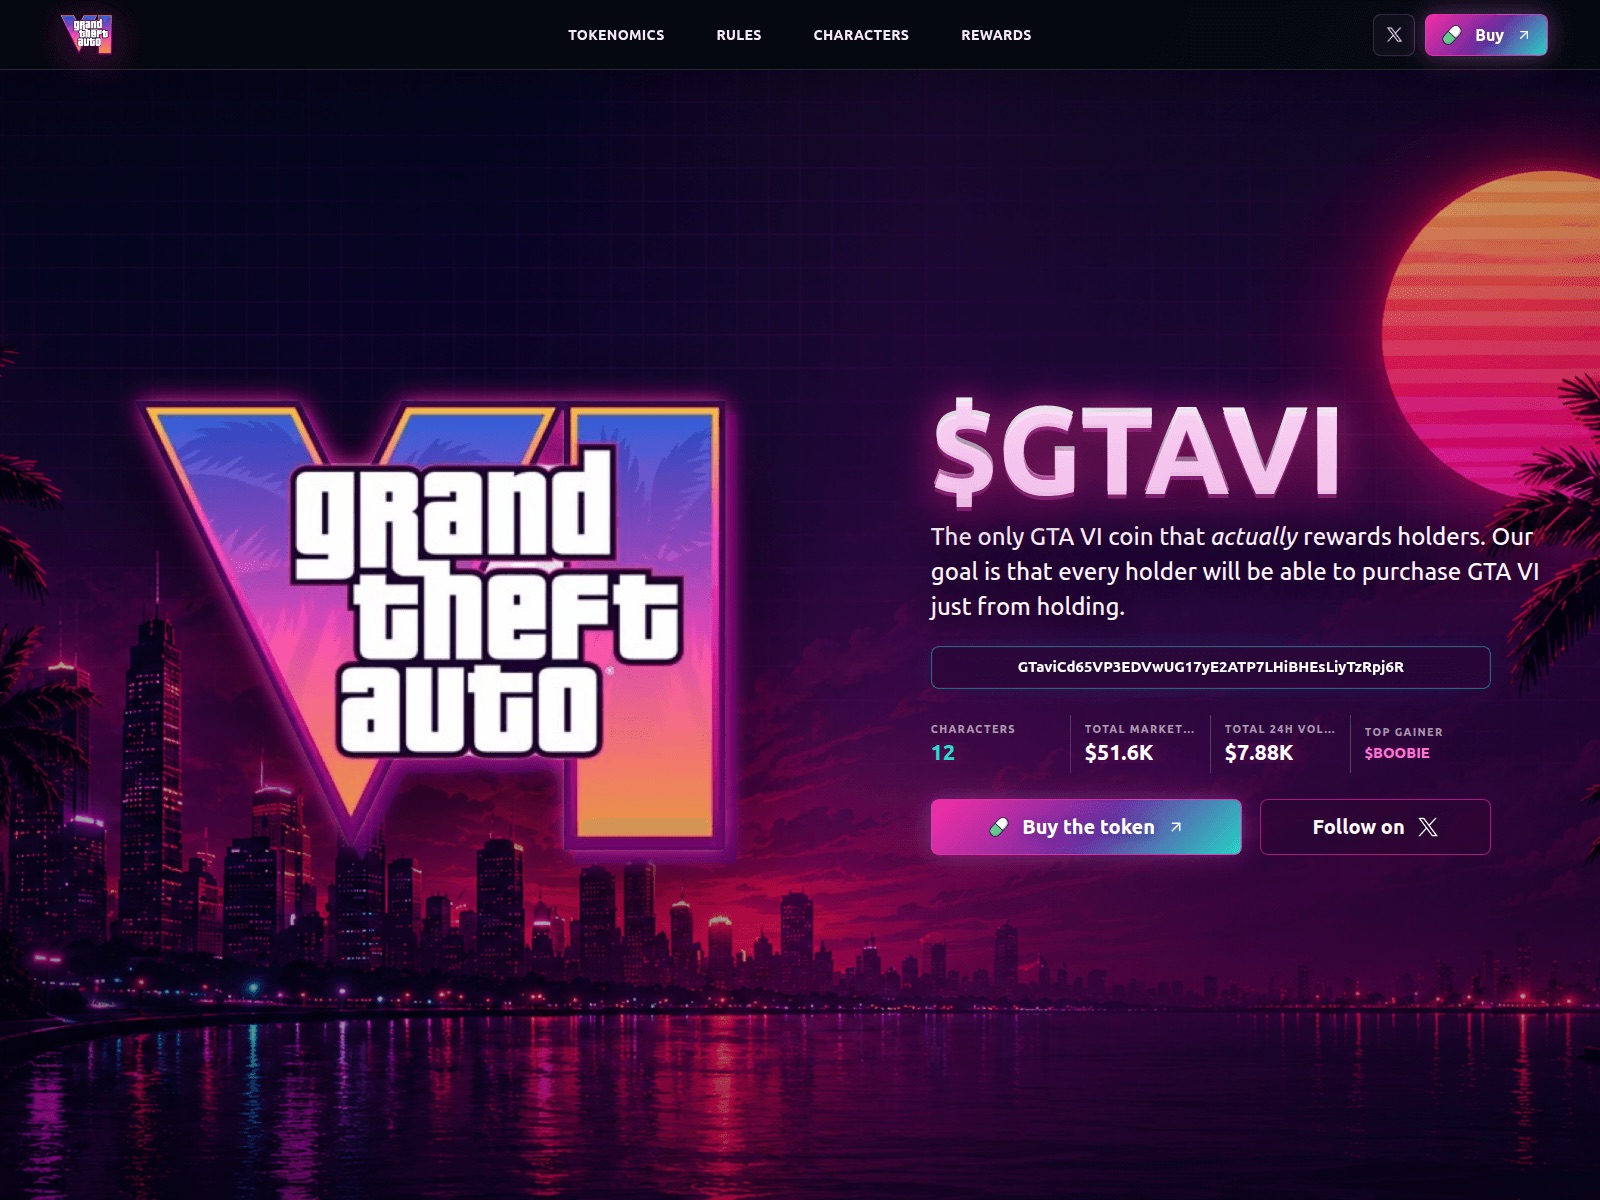
GTA VI as a reward for holding $GTAVI

The token’s creators claim that they’re striving to eventually provide every $GTAVI holder with access to GTA VI

To add a bit of credibility, the page also throws in some crypto stats. The claimed market cap of $GTAVI is 51,600 dollars, with a 24-hour trading volume of 7880 dollars. There’s also a mysterious metric called β€œCharacters” with a value of 12, and what exactly it means is anyone’s guess. There’s also a separate mention of a certain $BOOBIE as the Top GainerΒ β€” apparently, this is how the site’s creators labeled whoever supposedly made the most money off $GTAVI. The site doesn’t explain where any of these numbers come from or how accurate they actually are.

All in all, this looks like an attempt to hype up yet another meme coin by riding the wave of GTA VI’s popularity. Projects like this often end up following the classic pump-and-dump playbook: the token gets promoted for a while to drive its price up, and then the insiders and major holders cash out, leaving everyone else stuck with heavily devalued crypto. As for the stated goal behind $GTAVI β€” letting every token holder get a copy of GTA VI just for owning it β€” the site gives us no reason to believe that’s actually going to happen.

How to wait for GTA VI without falling for scammers

Unfortunately, we don’t know of a legitimate way to get early access to GTA VI, and honestly, we doubt anyone else does either. It looks like we’ll all just have to wait until November. To make sure you don’t fall for tempting scam offers in the meantime, here’s what we recommend:

  • Only install games from official sources.
  • Check the website address. Even if a page looks like the official Rockstar Games website or the PlayStation Store, carefully examine the domain in the address bar.
  • Never enter your payment details on sites promising GTA VI before its official release β€” especially if they ask you to pay in some unusual way like with cryptocurrency.
  • Don’t download unknown launchers, archives, or installation files, even if they’re billed as a β€œleaked build” or as software you need in order to be a beta tester.
  • Don’t hand over your personal information for a β€œbeta test”, β€œkey”, β€œearly access”, or any other offer that sounds too good to be true.
  • Never disable security features just because a website tells you to. If a site asks you to ignore a Windows warning, run some mysterious command, or launch an unknown file as an administrator, treat it as a giant red flag.
  • Install a reliable security solution built for gamers, one that warns you before you land on a scam site and blocks malicious files, but won’t slow your games down.

What other tricks do scammers pull to fool even the tech-savviest gamers? Find out in our other posts:

Bad Habits: An ANTISOC Operation

ANTISOC uses a mix of techniques from traditional penetration tests like red teams, cloud, web applications, externals, internals, and, of course, social engineering. We combine this mix of techniques with a wide-open scope, with the goal of going beyond what a typical pentest can discover.

The post Bad Habits: An ANTISOC Operation appeared first on Black Hills Information Security, Inc..

The game is over: when β€œfree” comes at too high a price. What we know about RenEngine

11 February 2026 at 15:00

We often describe cases of malware distribution under the guise of game cheats and pirated software. Sometimes such methods are used to spread complex malware that employs advanced techniques and sophisticated infection chains.

In February 2026, researchers from Howler Cell announced the discovery of a mass campaign distributing pirated games infected with a previously unknown family of malware. It turned out to be a loader called RenEngine, which was delivered to the device using a modified version of the Ren’Py engine-based game launcher. Kaspersky solutions detect the RenEngine loader as Trojan.Python.Agent.nb and HEUR:Trojan.Python.Agent.gen.

However, this threat is not new. Our solutions began detecting the first samples of the RenEngine loader in March 2025, when it was used to distribute the Lumma stealer (Trojan-PSW.Win32.Lumma.gen).

In the ongoing incidents, ACR Stealer (Trojan-PSW.Win32.ACRstealer.gen) is being distributed as the final payload. We have been monitoring this campaign for a long time and will share some details in this article.

Incident analysis

Disguise as a visual novel

Let’s look at the first incident, which we detected in March 2025. At that time, the attackers distributed the malware under the guise of a hacked game on a popular gaming web resource.

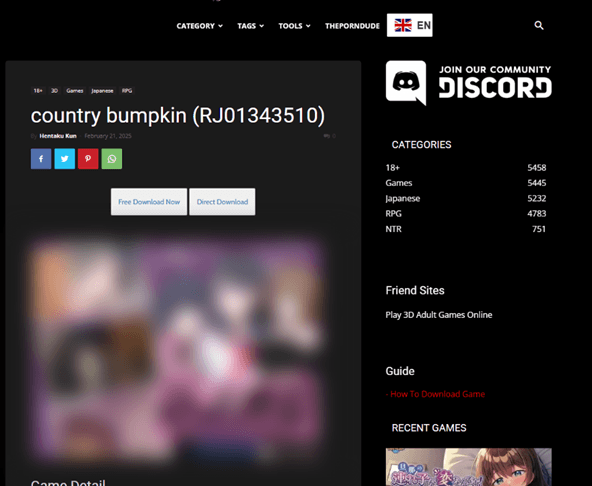
The website featured a game download page with two buttons: Free Download Now and Direct Download. Both buttons had the same functionality: they redirected users to the MEGA file-sharing service, where they were offered to download an archive with the β€œgame.”

Game download page

Game download page


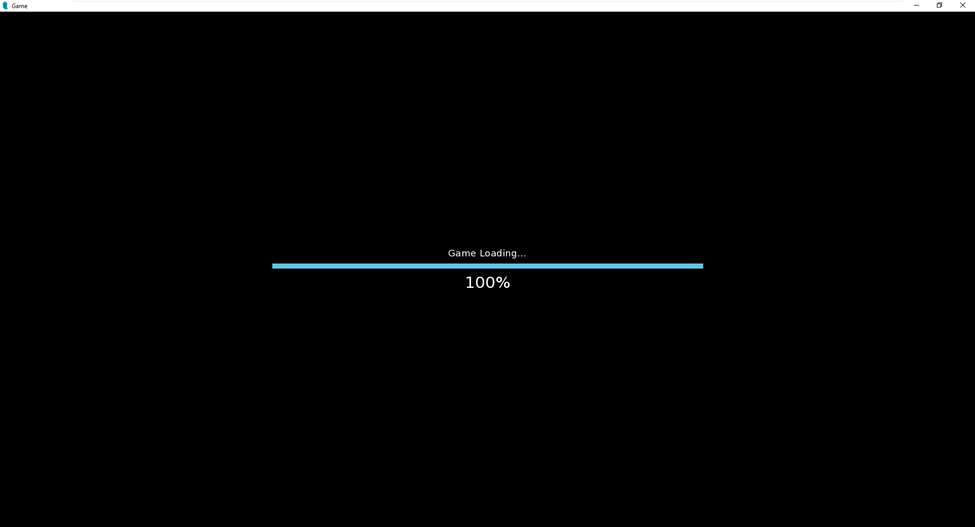
When the β€œgame” was launched, the download process would stop at 100%. One might think that the game froze, but that was not the case β€” the β€œreal” malicious code just started working.
Placeholder with the download screen

Placeholder with the download screen

β€œGame” source files analysis

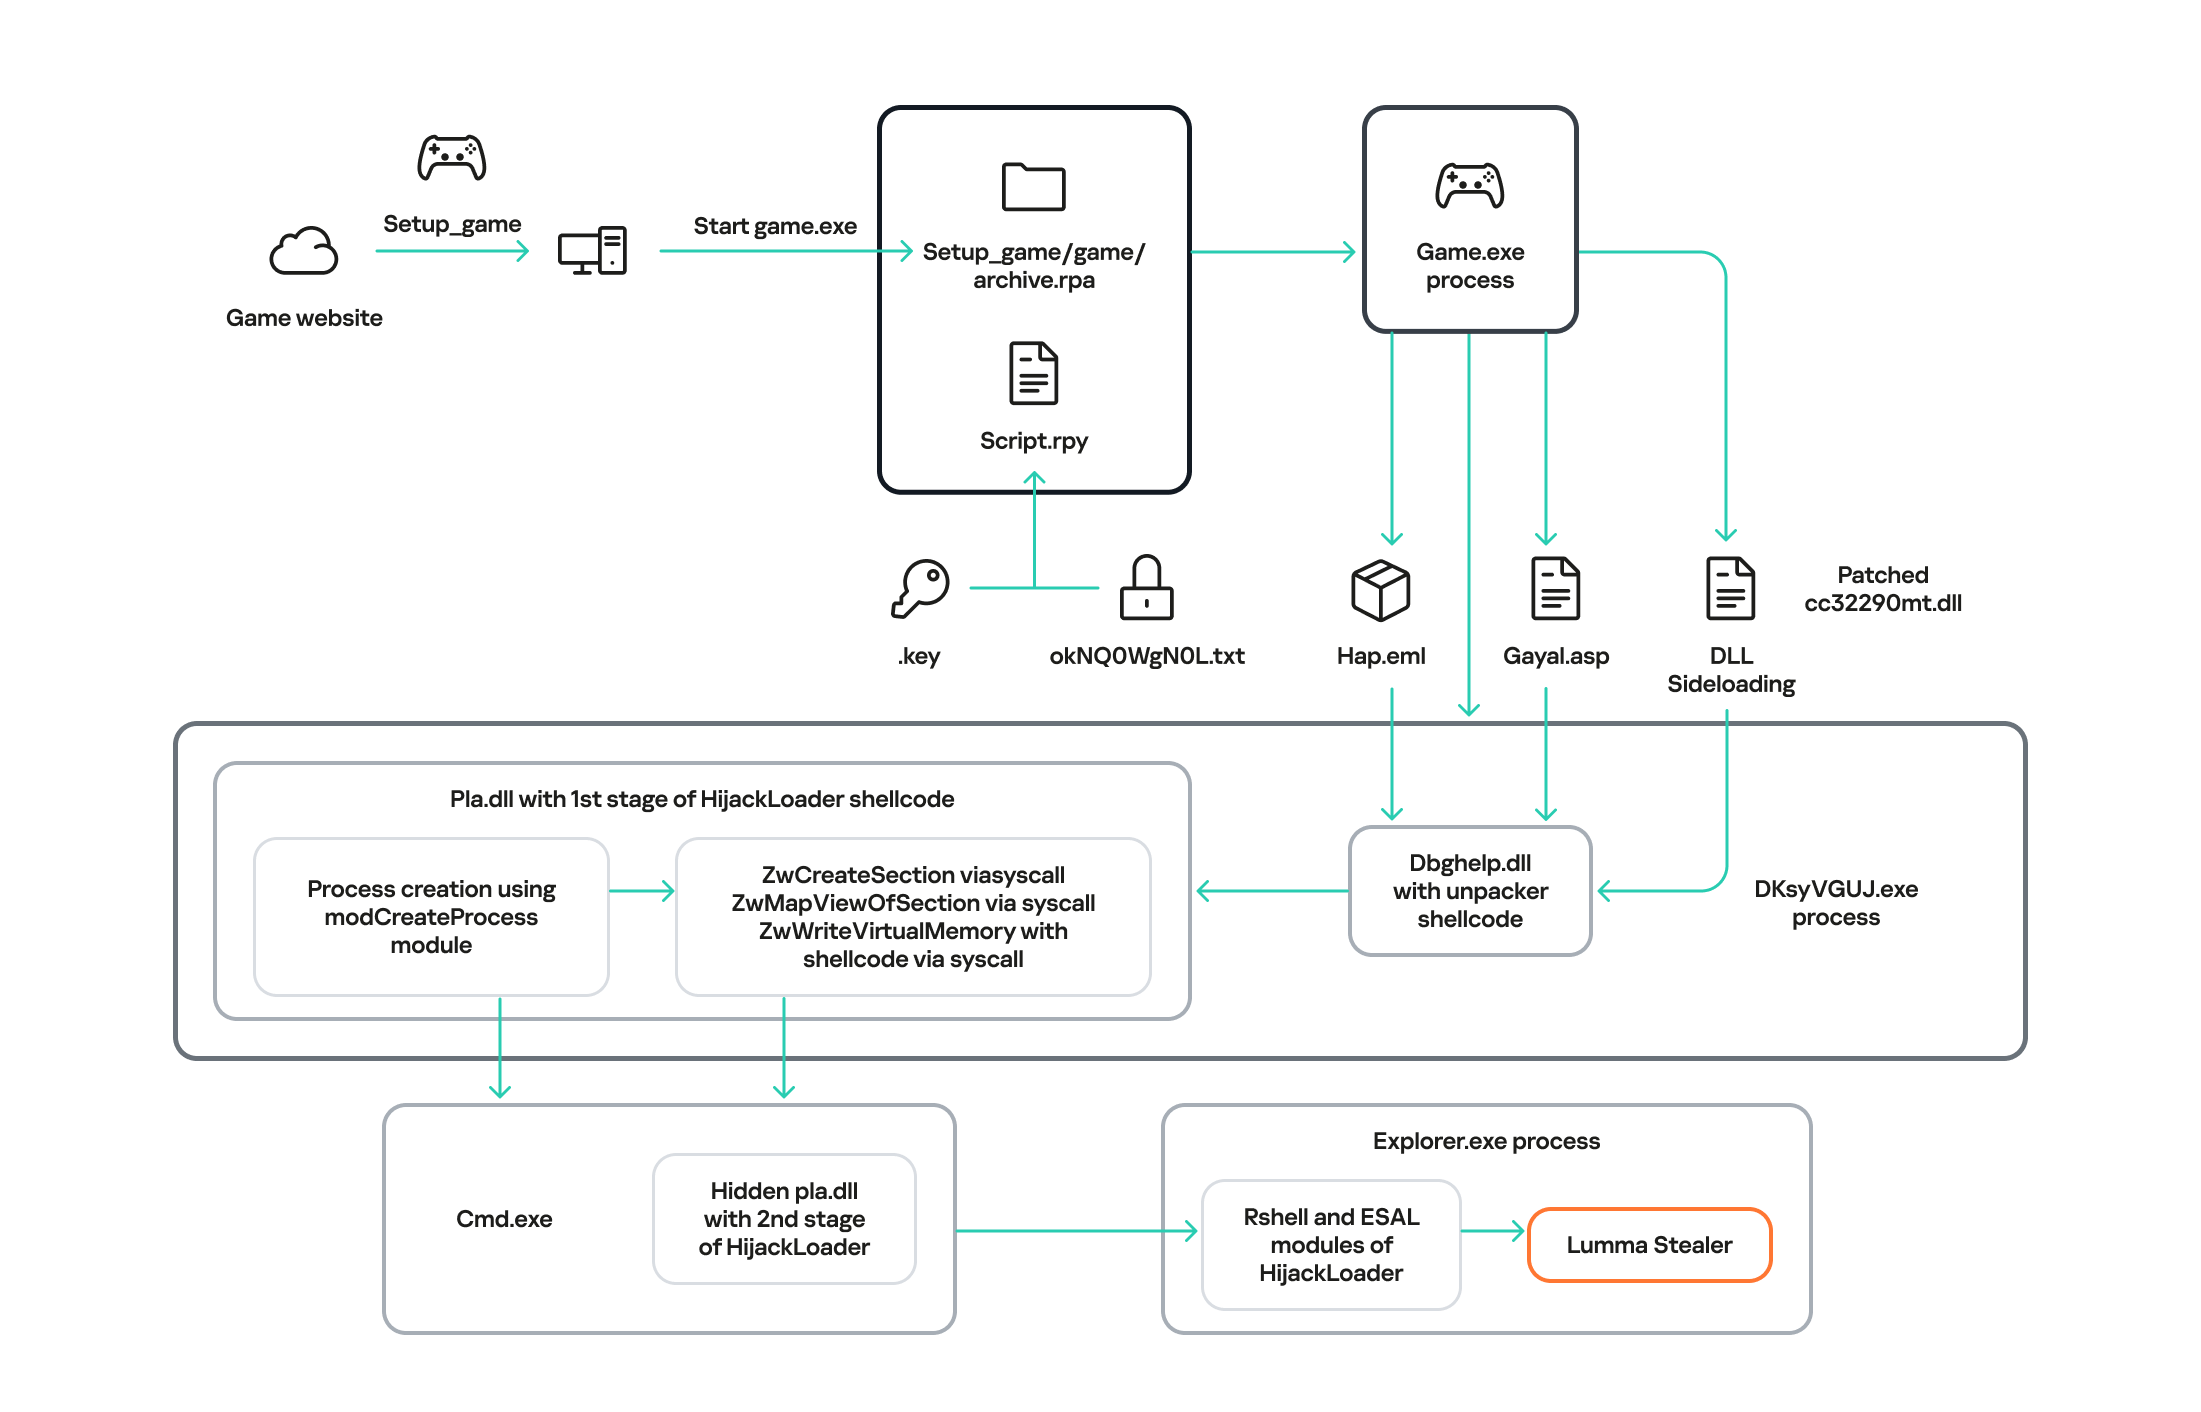
The full infection chain

The full infection chain


After analyzing the source files, we found Python scripts that initiated the initial device infection. These scripts imitated the endless loading of the game. In addition, they contained the is_sandboxed function for bypassing the sandbox and xor_decrypt_file for decrypting the malicious payload. Using the latter, the script decrypts the ZIP archive, unpacks its contents into the .temp directory, and launches the unpacked files.
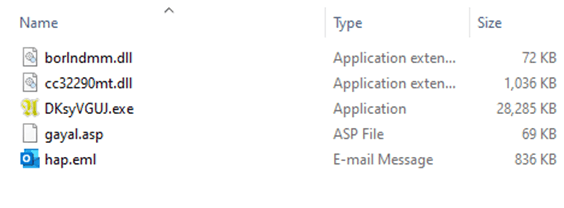
Contents of the .temp directory

Contents of the .temp directory


There are five files in the .temp directory. The DKsyVGUJ.exe executable is not malicious. Its original name is Ahnenblatt4.exe, and it is a well-known legitimate application for organizing genealogical data. The borlndmm.dll library also does not contain malicious code; it implements the memory manager required to run the executable. Another library, cc32290mt.dll, contains a code snippet patched by attackers that intercepts control when the application is launched and deploys the first stage of the payload in the process memory.

HijackLoader

The dbghelp.dll system library is used as a β€œcontainer” to launch the first stage of the payload. It is overwritten in memory with decrypted shellcode obtained from the gayal.asp file using the cc32290mt.dll library. The resulting payload is HijackLoader. This is a relatively new means of delivering and deploying malicious implants. A distinctive feature of this malware family is its modularity and configuration flexibility. HijackLoader was first detected and described in the summer of 2023. More detailed information about this loader is available to customers of the Kaspersky Intelligence Reporting Service.

The final payload can be delivered in two ways, depending on the configuration parameters of the malicious sample. The main HijackLoader ti module is used to launch and prepare the process for the final payload injection. In some cases, an additional module is also used, which is injected into an intermediate process launched by the main one. The code that performs the injection is the same in both cases.

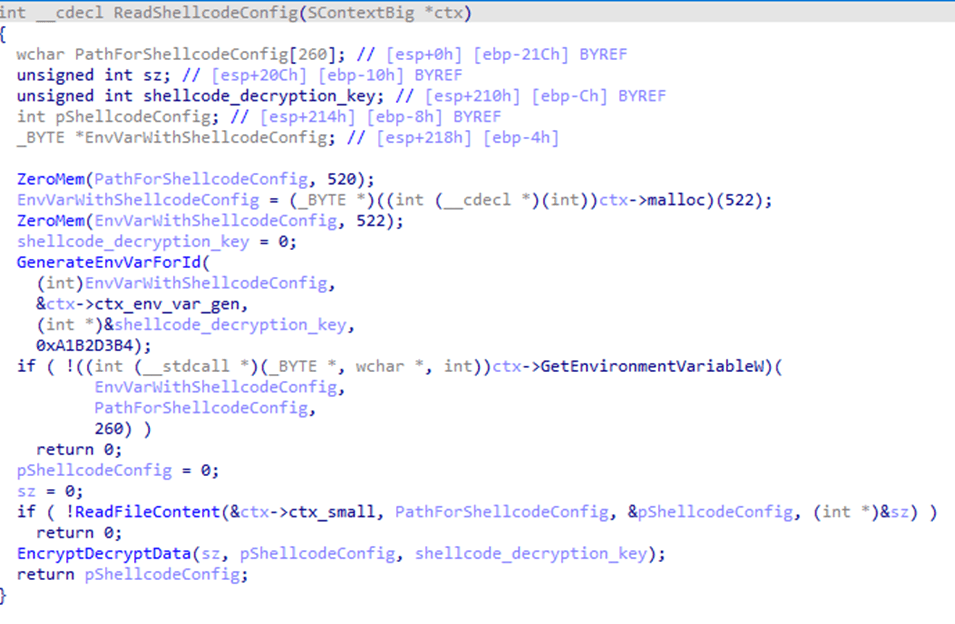
Before creating a child process, the configuration parameters are encrypted using XOR and saved to the %TEMP% directory with a random name. The file name is written to the system environment variables.

Loading configuration parameters saved by the main module

Loading configuration parameters saved by the main module


In the analyzed sample, the execution follows a longer path with an intermediate child process, cmd.exe. It is created in suspended mode by calling the auxiliary module modCreateProcess. Then, using the ZwCreateSection and ZwMapViewOfSection system API calls, the code of the same dbghelp.dll library is loaded into the address space of the process, after which it intercepts control.

Next, the ti module, launched inside the child process, reads the hap.eml file, from which it decrypts the second stage of HijackLoader. The module then loads the pla.dll system library and overwrites the beginning of its code section with the received payload, after which it transfers control to this library.

Payload decryption

Payload decryption


The decrypted payload is an EXE file, and the configuration parameters are set to inject it into the explorer.exe child process. The payload is written to the memory of the child process in several stages:
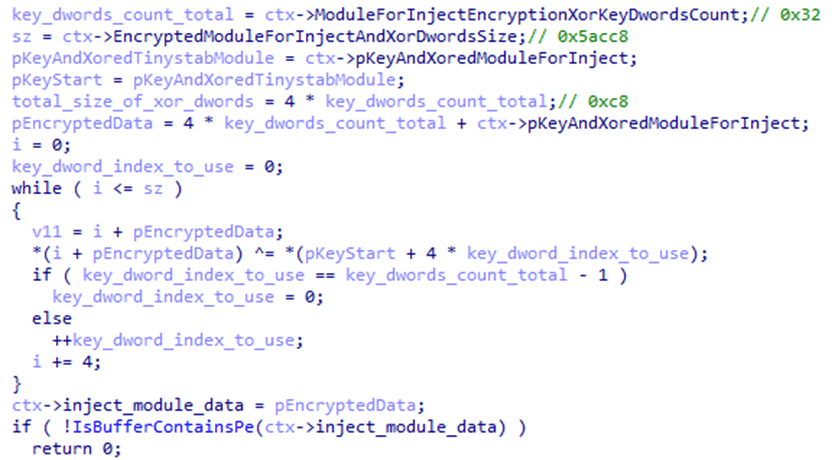
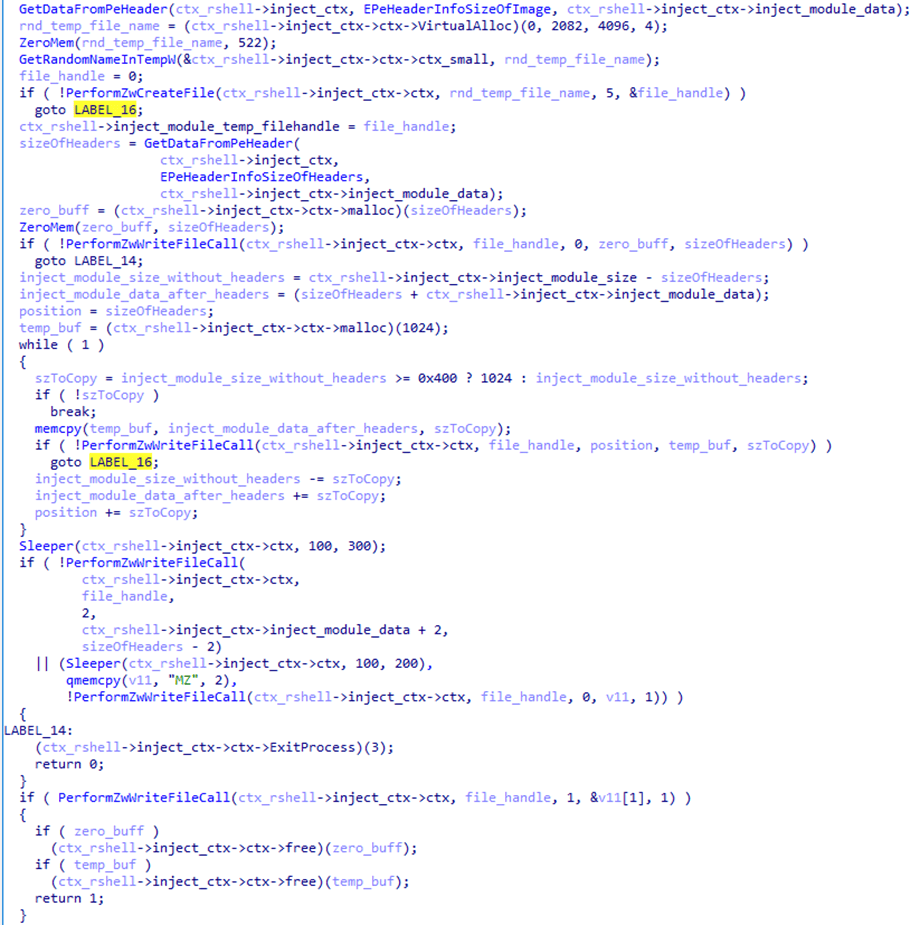
  1. First, the malicious payload is written to a temporary file on disk using the transaction mechanism provided by the Windows API. The payload is written in several stages and not in the order in which the data is stored in the file. The MZ signature, with which any PE file begins, is written last with a delay.
    Writing the payload to a temporary file

    Writing the payload to a temporary file

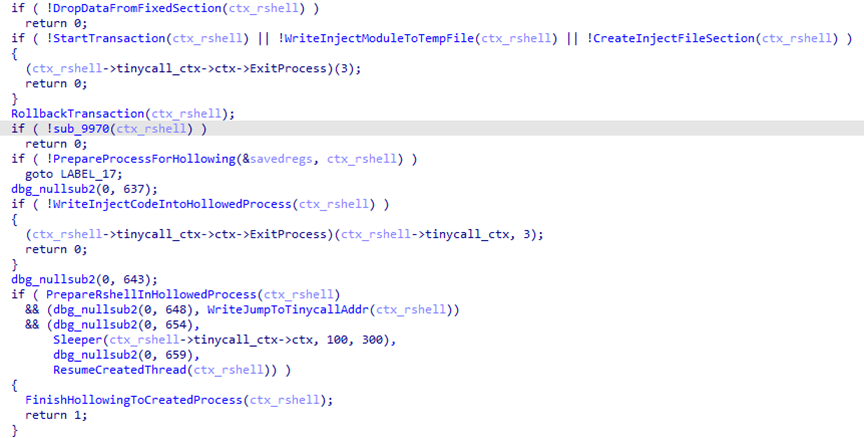
  2. After that, the payload is loaded from the temporary file into the address space of the current process using the ZwCreateSection call. The transaction that wrote to the file is rolled back, thus deleting the temporary file with the payload.
  3. Next, the sample uses the modCreateProcess module to launch the child process explorer.exe and injects the payload into it by creating a shared memory region with the ZwMapViewOfSection call.
    Payload injection into the child process

    Payload injection into the child process


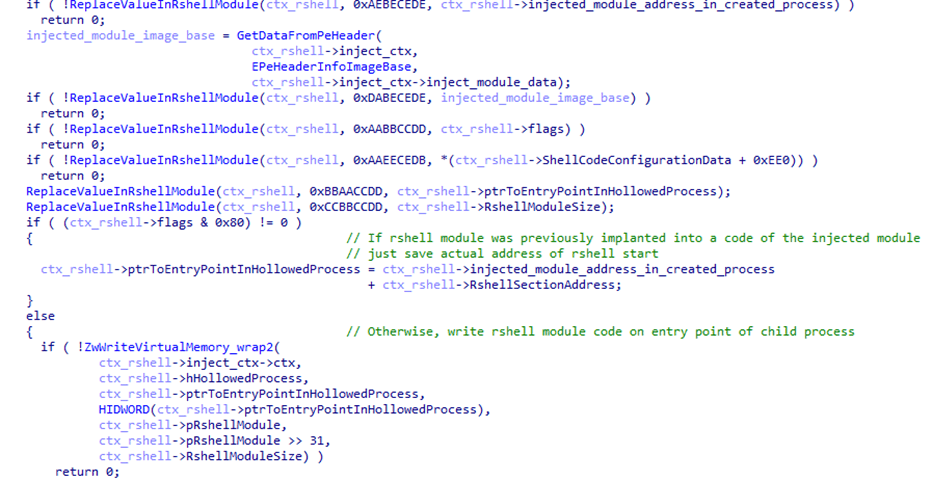
    Another HijackLoader module, rshell, is used to launch the shellcode. Its contents are also injected into the child process, replacing the code located at its entry point.
    The rshell module injection

    The rshell module injection

  4. The last step performed by the parent process is starting a thread in the child process by calling ZwResumeThread. After that, the thread starts executing the rshell module code placed at the child process entry point, and the parent process terminates.

    The rshell module prepares the final malicious payload. Once it has finished, it transfers control to another HijackLoader module called ESAL. It replaces the contents of rshell with zeros using the memset function and launches the final payload, which is a stealer from the Lumma family (Trojan-PSW.Win32.Lumma).

In addition to the modules described above, this HijackLoader sample contains the following modules, which were used at intermediate stages: COPYLIST, modTask, modUAC, and modWriteFile.
Kaspersky solutions detect HijackLoader with the verdicts Trojan.Win32.Penguish and Trojan.Win32.DllHijacker.

Not only games

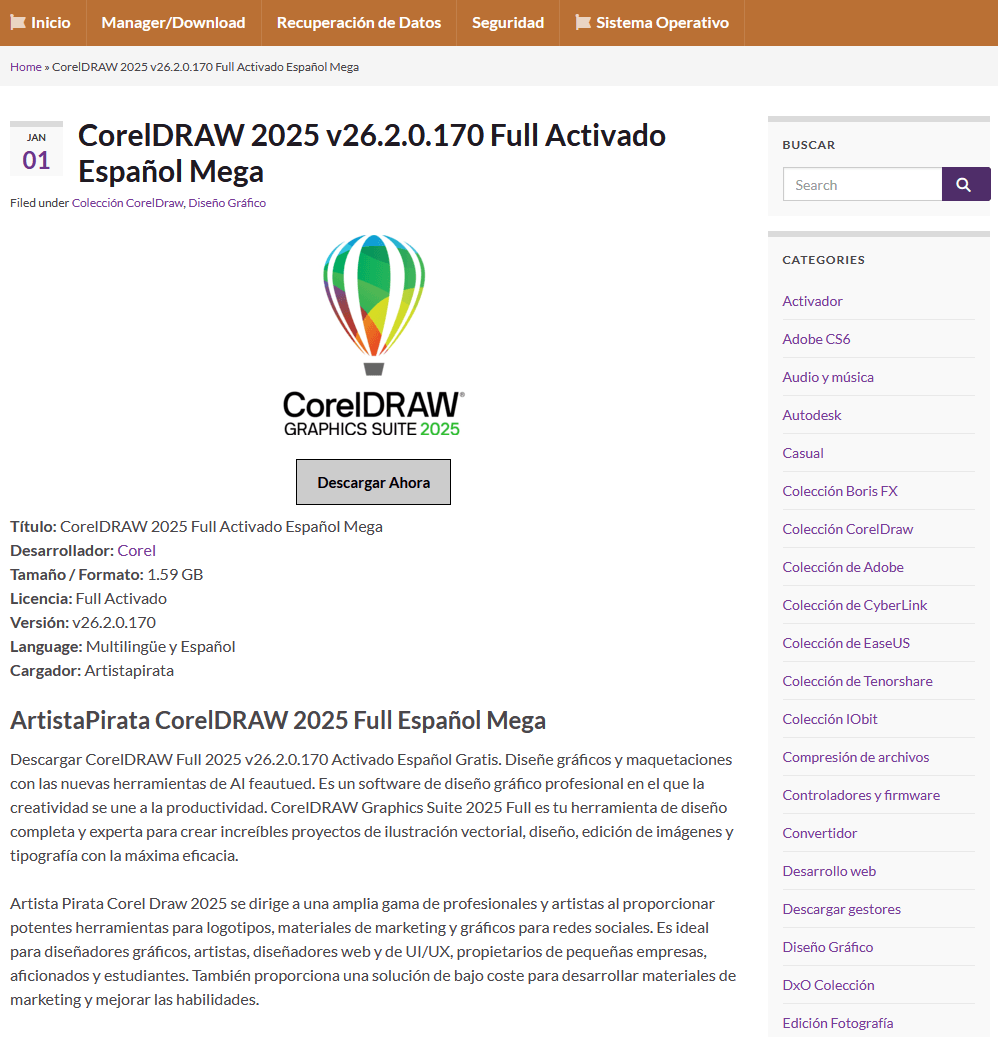
In addition to gaming sites, we found that attackers created dozens of different web resources to distribute RenEngine under the guise of pirated software. On one such site, for example, users can supposedly download an activated version of the CorelDRAW graphics editor.

Distribution of RenEngine under the guise of the CorelDRAW pirated version

Distribution of RenEngine under the guise of the CorelDRAW pirated version


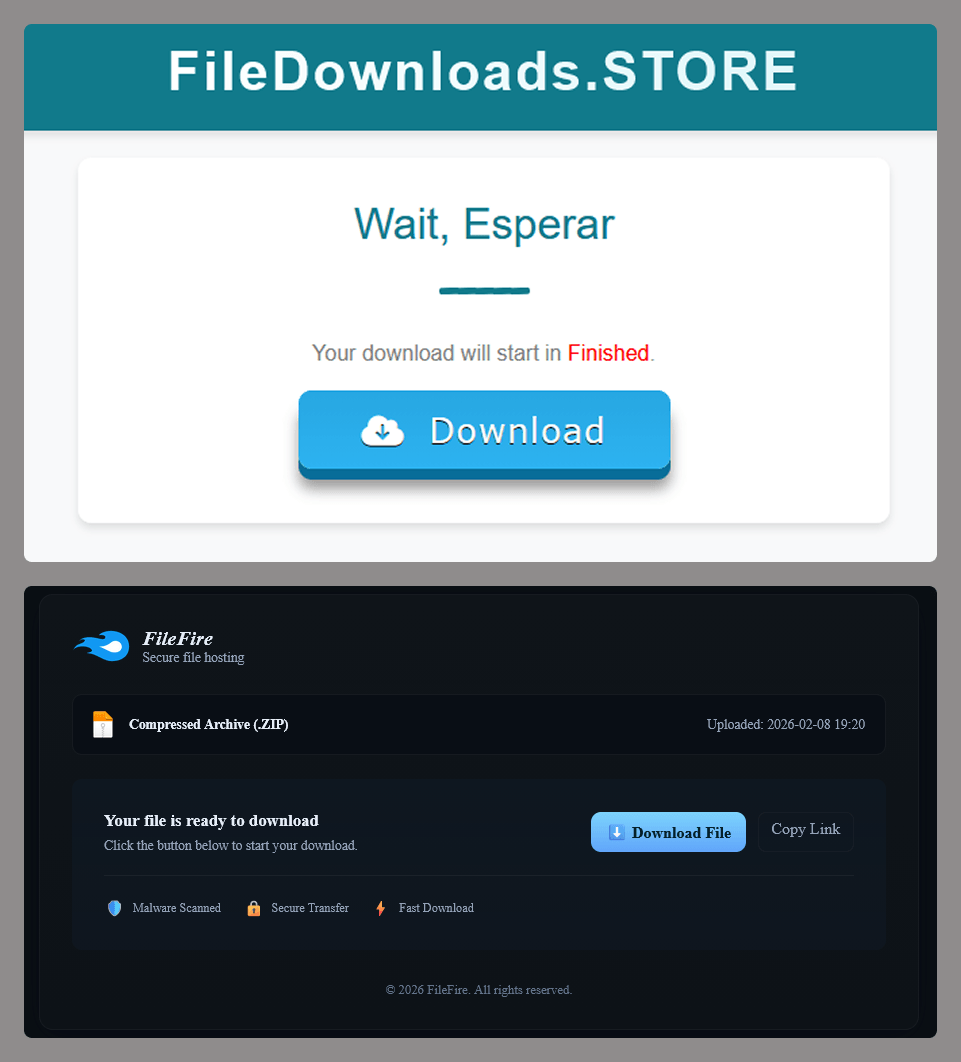
When the user clicks the Descargar Ahora (β€œDownload Now”) button, they are redirected several times to other malicious websites, after which an infected archive is downloaded to their device.
File storage imitations

File storage imitations

Distribution

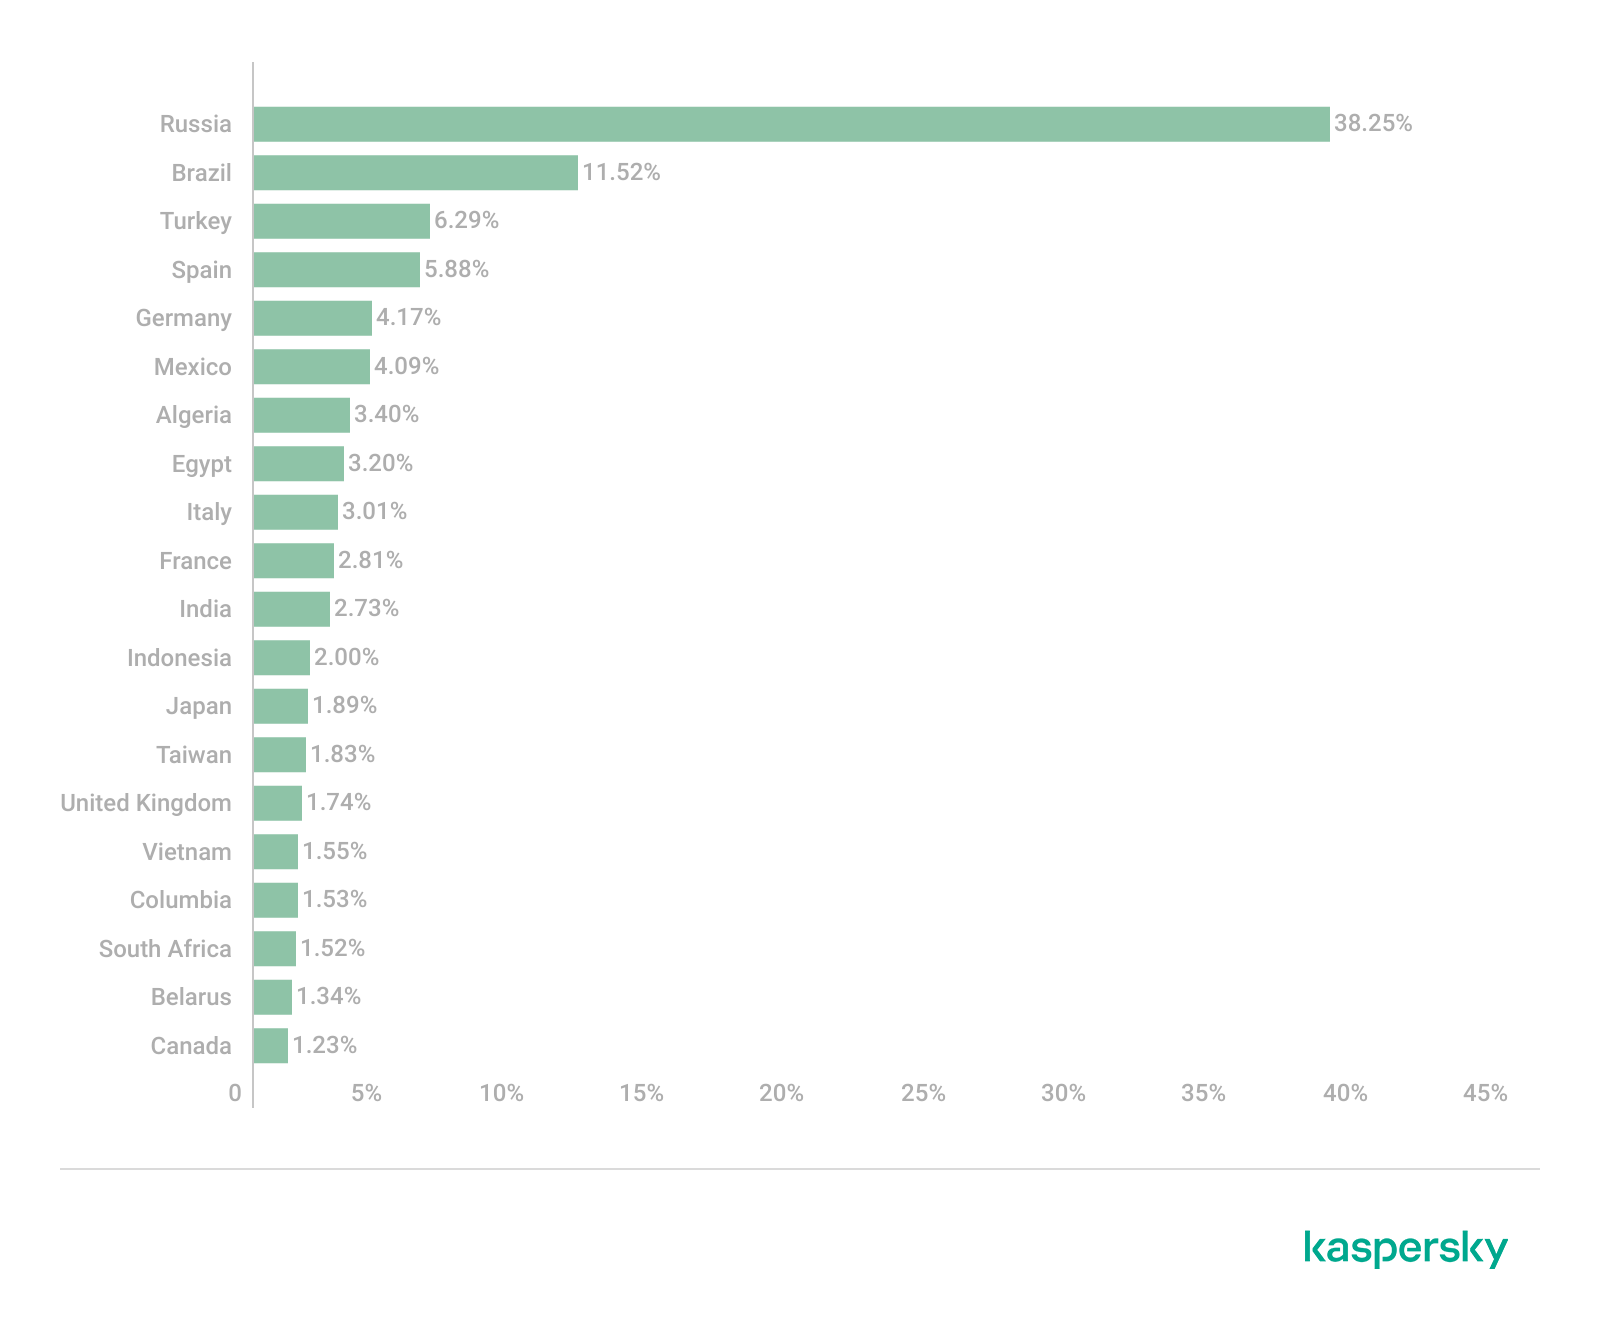
According to our data, since March 2025, RenEngine has affected users in the following countries:

Distribution of incidents involving the RenEngine loader by country (TOP 20), February 2026 (download)

The distribution pattern of this loader suggests that the attacks are not targeted. At the time of publication, we have recorded the highest number of incidents in Russia, Brazil, TΓΌrkiye, Spain, and Germany.

Recommendations for protection

The format of game archives is generally not standardized and is unique for each game. This means that there is no universal algorithm for unpacking and checking the contents of game archives. If the game engine does not check the integrity and authenticity of executable resources and scripts, such an archive can become a repository for malware if modified by attackers. Despite this, Kaspersky Premium protects against such threats with its Behavior Detection component.

The distribution of malware under the guise of pirated software and hacked games is not a new tactic. It is relatively easy to avoid infection by the malware described in this article: simply install games and programs from trusted sites. In addition, it is important for gamers to remember the need to install specialized security solutions. This ongoing campaign employs the Lumma and ACR stylers, and Vidar was also found β€” none of these are new threats, but rather long-known malware. This means that modern antivirus technologies can detect even modified versions of the above-mentioned stealers and their alternatives, preventing further infection.

Indicators of compromise

12EC3516889887E7BCF75D7345E3207A – setup_game_8246.zip
D3CF36C37402D05F1B7AA2C444DC211A – __init.py__
1E0BF40895673FCD96A8EA3DDFAB0AE2 – cc32290mt.dll
2E70ECA2191C79AD15DA2D4C25EB66B9 – Lumma Stealer

hxxps://hentakugames[.]com/country-bumpkin/
hxxps://dodi-repacks[.]site
hxxps://artistapirata[.]fit
hxxps://artistapirata[.]vip
hxxps://awdescargas[.]pro
hxxps://fullprogramlarindir[.]me
hxxps://gamesleech[.]com
hxxps://parapcc[.]com
hxxps://saglamindir[.]vip
hxxps://zdescargas[.]pro
hxxps://filedownloads[.]store
hxxps://go[.]zovo[.]ink

Lumma C2
hxxps://steamcommunity[.]com/profiles/76561199822375128
hxxps://localfxement[.]live
hxxps://explorebieology[.]run
hxxps://agroecologyguide[.]digital
hxxps://moderzysics[.]top
hxxps://seedsxouts[.]shop
hxxps://codxefusion[.]top
hxxps://farfinable[.]top
hxxps://techspherxe[.]top
hxxps://cropcircleforum[.]today

Join Us for Camp BHIS @ DEF CON 31Β 

Hey, Campers! It’s that time of year again. The smell of 0-day in the air. Charlatans roasting by the pyre. Old friends and new gather in one of the worst […]

The post Join Us for Camp BHIS @ DEF CON 31Β  appeared first on Black Hills Information Security, Inc..

POGS at Wild West Hackin’ Fest!Β 

Ean Meyer // This post is for attendees of Wild West Hackin’ Fest: Deadwood 2022 POGs? Yes, POGs! If you aren’t familiar with POGs, this game started decades ago, reaching […]

The post POGS at Wild West Hackin’ Fest!Β  appeared first on Black Hills Information Security, Inc..

Talkin’ About Infosec News – 10/5/2022

By: BHIS
5 October 2022 at 23:21

02:28 – Story # 1: American Airlines Breach Exposes Customer and Staff Information– https://www.infosecurity-magazine.com/news/american-airlines-breach-customer/18:59 – Story # 2: London police arrest, charge teen hacking suspect but won’t confirm GTA 6, Uber […]

The post Talkin’ About Infosec News – 10/5/2022 appeared first on Black Hills Information Security, Inc..

πŸ’Ύ

So You Want to Build a Conference Hardware Badge!

Ray Felch // Recently, it was suggested that it would be cool to create a hardware badge for one of the upcoming InfoSec conferences. Admittedly, I have a pretty solid […]

The post So You Want to Build a Conference Hardware Badge! appeared first on Black Hills Information Security, Inc..

Webcast: How to Share Your Knowledge with Others

By: BHIS
2 November 2021 at 18:22

Have you ever seen a call for papers for a conference and thought to yourself that you’d like to submit a talk and then immediately thought, oh never mind? Have […]

The post Webcast: How to Share Your Knowledge with Others appeared first on Black Hills Information Security, Inc..

πŸ’Ύ

The Birth of PreShowBanterCon-A-Thon 2021!β„’

Join the BHIS Community Discord: https://discord.gg/bhis Music By Beau: https://www.nobandwidth.io 00:00 – 2021-04-01 – PreShow Banterβ„’ β€” Intro Sec Con & The Birth of PreShowBanterCon-A-Thon 2021!β„’ 05:29 – You’re So […]

The post The Birth of PreShowBanterCon-A-Thon 2021!β„’ appeared first on Black Hills Information Security, Inc..

πŸ’Ύ

Backdoors & Breaches LIVE – 5/19/2021

Join our Incident Master Ean Meyer as we play another round of Backdoors & Breaches (B&B) session using our new Tabletop Simulator (TTS) version! If you have STEAM / TABLETOP […]

The post Backdoors & Breaches LIVE – 5/19/2021 appeared first on Black Hills Information Security, Inc..

πŸ’Ύ

Using SDR to Build a Trunk Tracker – Police, Fire, and EMS Scanner

Ray Felch // IntroductionΒ  Recently, I came across an interesting article on using software-defined radio (SDR) to create aΒ Police, Fire,Β EMS,Β and Public Safety systems scanner. Viewing a few of these Trunk […]

The post Using SDR to Build a Trunk Tracker – Police, Fire, and EMS Scanner appeared first on Black Hills Information Security, Inc..

Information From Thin Air: Using SDR to Extract DTMF from Radio Waves

Ray Felch // DisclaimerΒ  When using an FM transmitter, do notΒ modifyΒ the intended operation of the module by amplifying the transmitted signal. Also, be sure that attaching an FM high gain […]

The post Information From Thin Air: Using SDR to Extract DTMF from Radio Waves appeared first on Black Hills Information Security, Inc..

Using Infrared for Hardware Control

Ray Felch // OverviewΒ  Infrared technology has been around for a very long time and is a wireless technology used in devices that convey data by way of Infrared radiation. […]

The post Using Infrared for Hardware Control appeared first on Black Hills Information Security, Inc..

Backdoors & Breaches LIVE – 3/10/2021

By: BHIS
18 March 2021 at 13:18

The Livestream of our first Backdoors & Breaches (B&B) session using our new Tabletop Simulator (TTS) version of the game was a success! If you have STEAM / TABLETOP SIMULATOR […]

The post Backdoors & Breaches LIVE – 3/10/2021 appeared first on Black Hills Information Security, Inc..

πŸ’Ύ

❌